Enterprise Wireless Security Lab — 802.1X + FortiGate + Cisco WLC
A full enterprise wireless security simulation in EVE-NG: 802.1X authentication through Windows NPS, a dual-SSID Cisco WLC deployment, FortiGate zone policies and Layer 2 hardening.محاكاة كاملة لأمن الشبكات اللاسلكية المؤسسية في EVE-NG: مصادقة 802.1X عبر Windows NPS، ونشر Cisco WLC بشبكتين لاسلكيتين، وسياسات مناطق FortiGate، وتحصين الطبقة الثانية.
Separate staff and guests, and authenticate each properlyفصل الموظفين عن الضيوف ومصادقة كل فئة بالشكل الصحيح
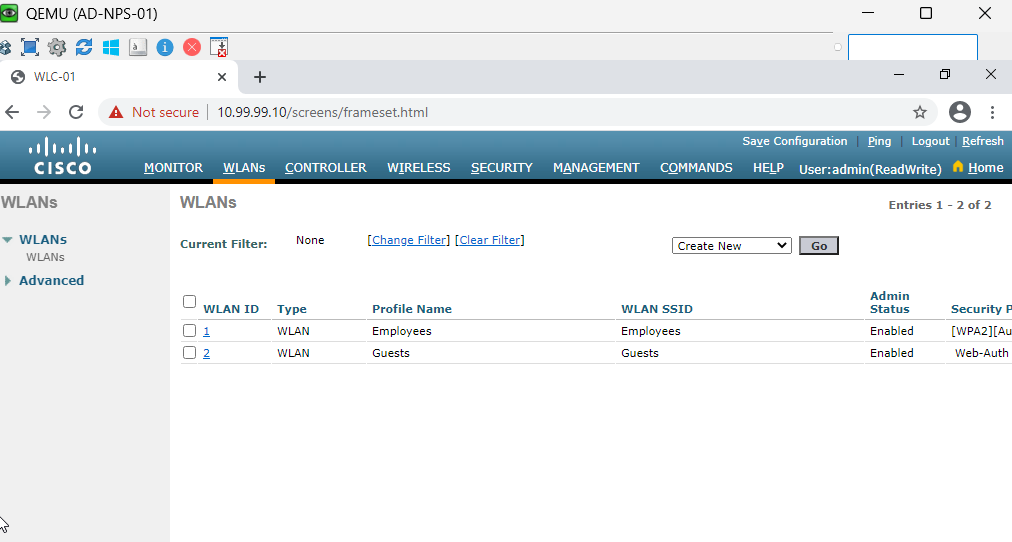
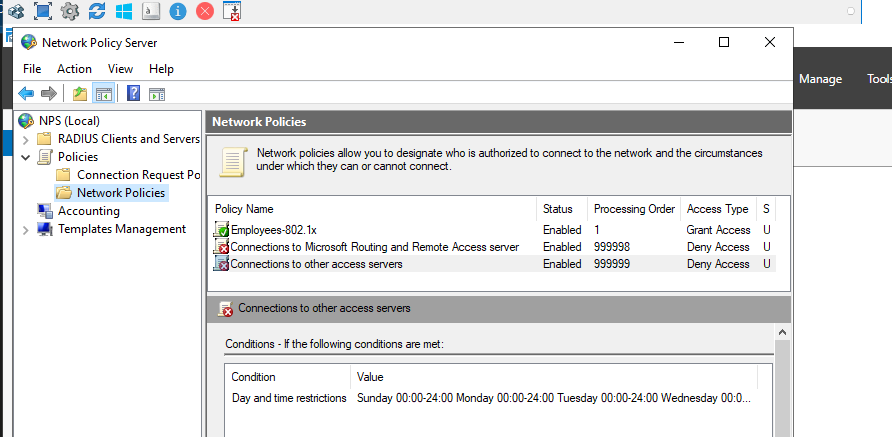
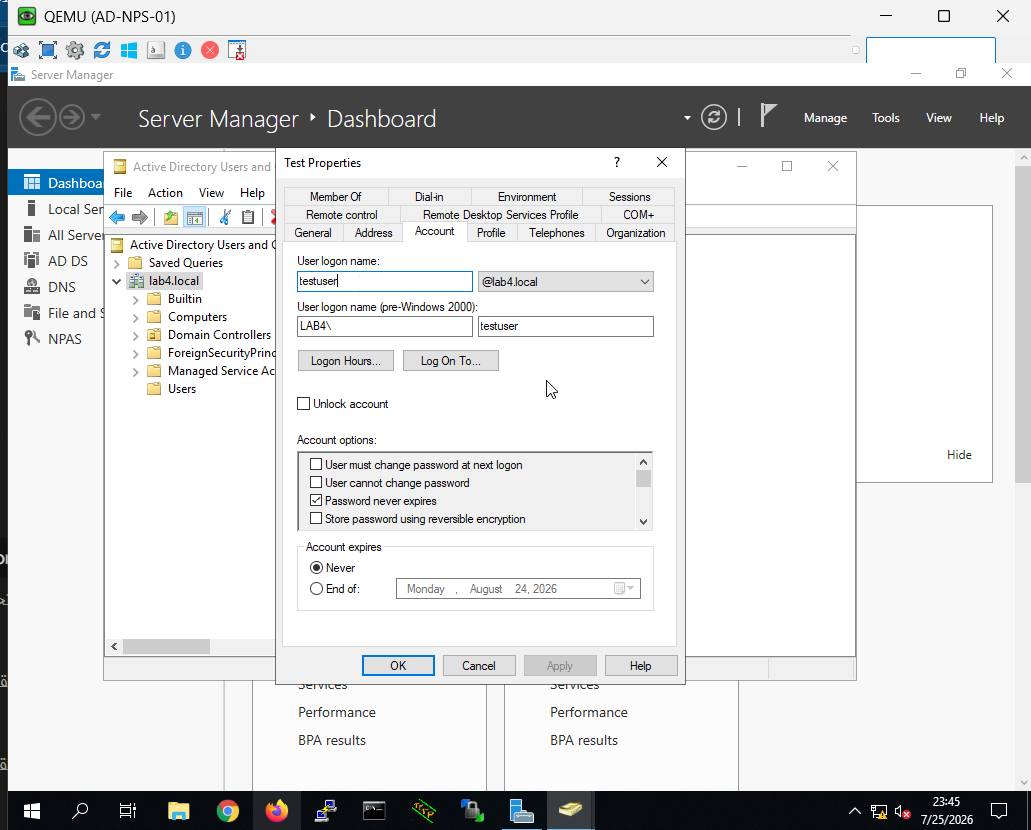
The lab models a company that offers two wireless networks. Employees connect with WPA2-Enterprise and 802.1X, authenticated against Active Directory through a Windows NPS RADIUS server. Guests connect through a Web-Auth captive portal on their own VLAN.يحاكي المختبر شركة لديها شبكتان لاسلكيتان. يتصل الموظفون بـWPA2-Enterprise و802.1X ويُصادَقون مقابل Active Directory عبر خادم RADIUS على Windows NPS. ويتصل الضيوف عبر بوابة Web-Auth على VLAN خاص بهم.
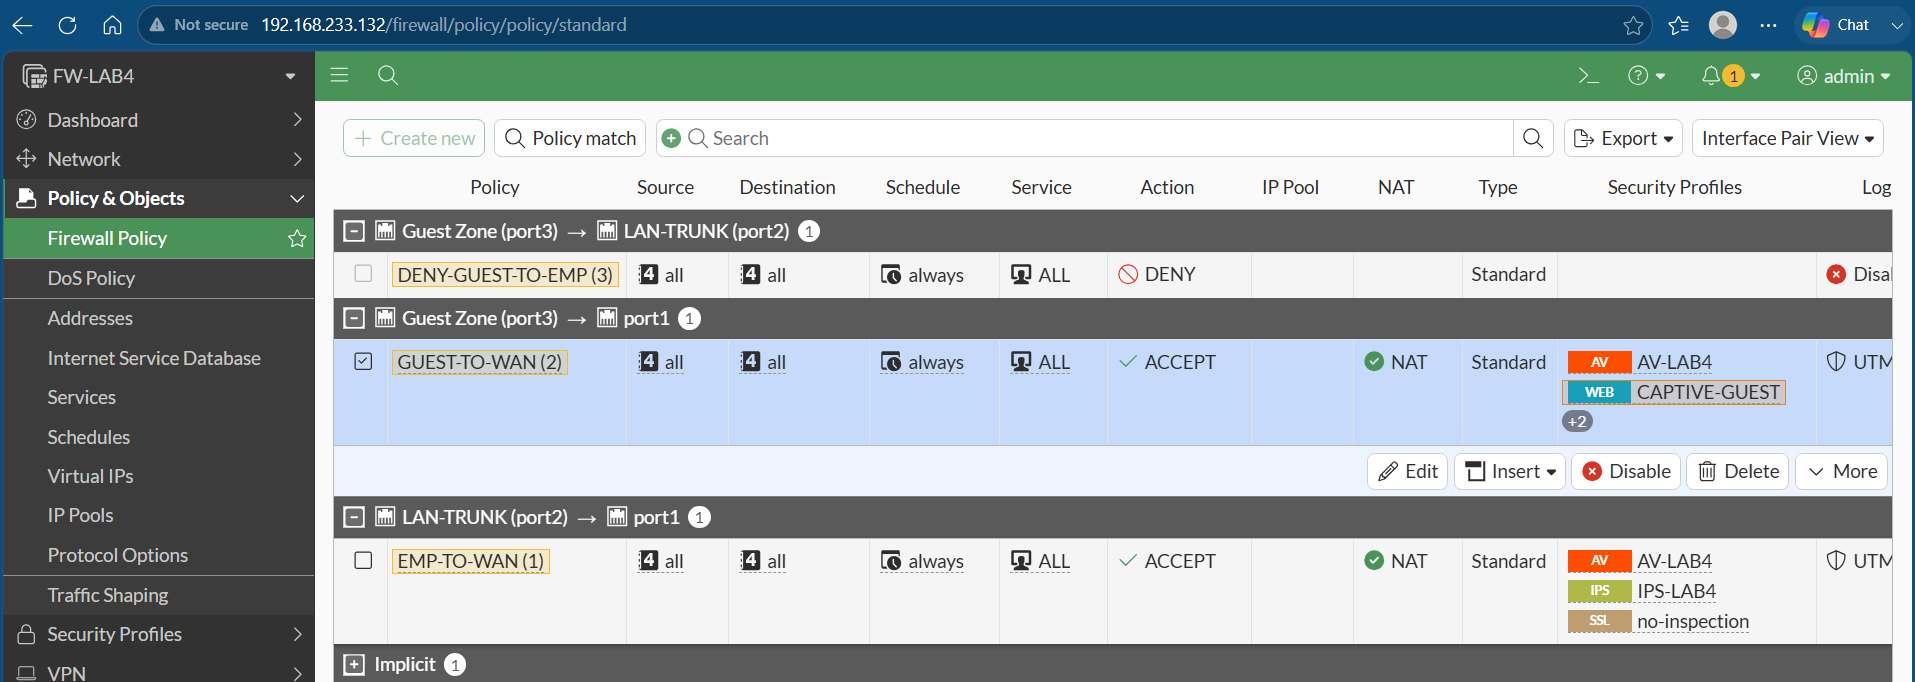
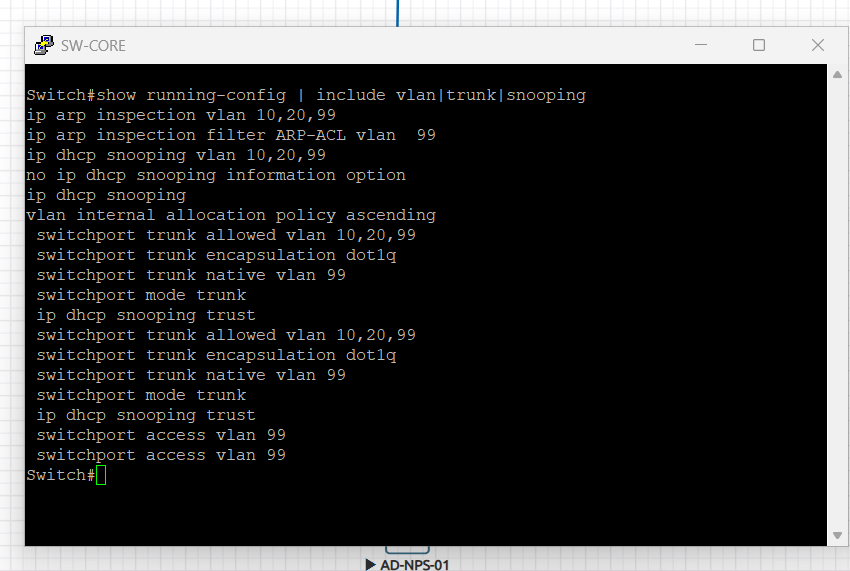
A FortiGate firewall applies zone-based policies, including guest isolation and AV, IPS and web filtering, and the core switch is hardened with DHCP Snooping and Dynamic ARP Inspection.يطبّق جدار FortiGate سياسات مبنية على المناطق تشمل عزل الضيوف ومكافحة الفيروسات وIPS وفلترة الويب، ويُحصَّن السويتش المركزي بـDHCP Snooping وDynamic ARP Inspection.
- Platformالمنصة
- EVE-NG
- Devicesالأجهزة
- FW-01 (FortiGate), SW-CORE (Cisco), WLC-01, AD-NPS-01, CLIENT-01FW-01 (FortiGate) وSW-CORE (Cisco) وWLC-01 وAD-NPS-01 وCLIENT-01
- VLANsشبكات VLAN
- 10 Employees · 20 Guests · 99 Management10 موظفون · 20 ضيوف · 99 إدارة
- Softwareالبرمجيات
- FortiOS 7.x, Cisco WLC, Windows NPS, Active DirectoryFortiOS 7.x وCisco WLC وWindows NPS وActive Directory
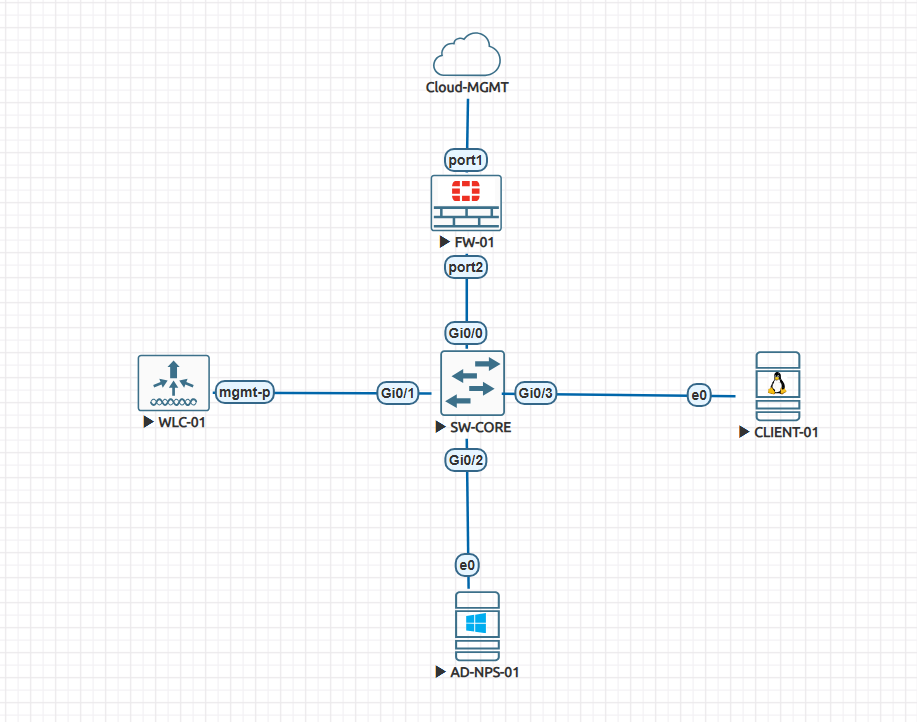
Topologyالطوبولوجيا
FW-01 (FortiGate) connects to SW-CORE (Cisco), which serves WLC-01, AD-NPS-01 and CLIENT-01.يتصل FW-01 (FortiGate) بـSW-CORE (Cisco) الذي يخدم WLC-01 وAD-NPS-01 وCLIENT-01.
What the lab coversما يغطيه المختبر
- 802.1X RADIUS authentication: Windows NPS as the RADIUS server, integrated with Active Directory.مصادقة 802.1X عبر RADIUS: خادم Windows NPS كخادم RADIUS متكامل مع Active Directory.
- Dual-SSID wireless: Employees on WPA2 with 802.1X and Guests on Web-Auth, on separate VLANs.شبكتان لاسلكيتان: الموظفون على WPA2 مع 802.1X، والضيوف على Web-Auth، في شبكتي VLAN منفصلتين.
- FortiGate zone-based policies: guest isolation, captive portal, and AV, IPS and web filtering.سياسات FortiGate المبنية على المناطق: عزل الضيوف وبوابة التسجيل ومكافحة الفيروسات وIPS وفلترة الويب.
- Layer 2 hardening: DHCP Snooping and Dynamic ARP Inspection on the VLANs.تحصين الطبقة الثانية: DHCP Snooping وDynamic ARP Inspection على شبكات VLAN.
Wireless and authenticationاللاسلكي والمصادقة
Firewall and Layer 2 securityالجدار الناري وأمان الطبقة الثانية
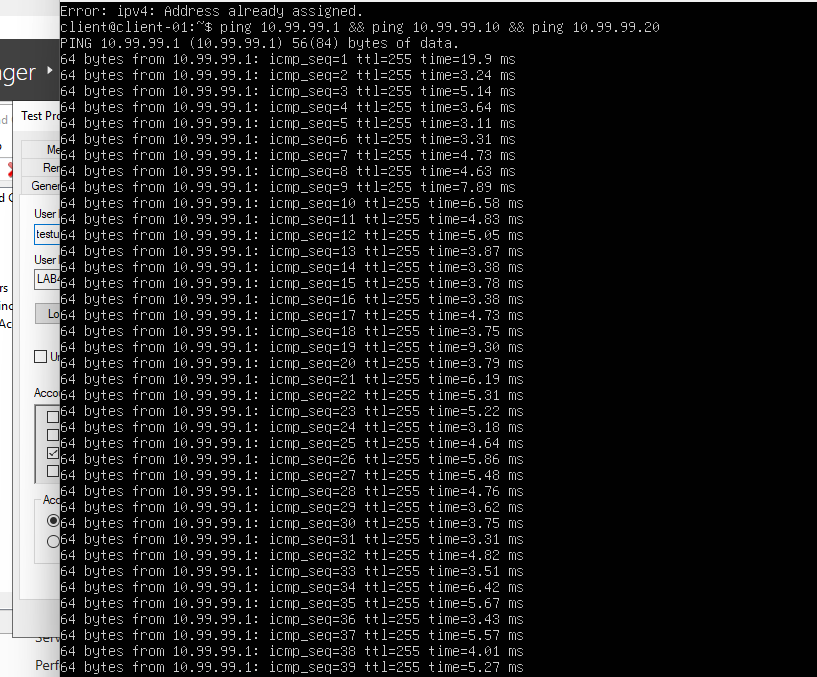
Client connectivityاتصال العميل
A client connected through the lab and a ping test completed with zero packet loss.اتصل عميل عبر المختبر واكتمل اختبار ping بدون أي فقدان في الحزم.
What this project showsما يُظهره هذا المشروع
- 802.1X and EAP authentication with a Windows NPS RADIUS server.مصادقة 802.1X وEAP مع خادم RADIUS على Windows NPS.
- Cisco WLC with WPA2-Enterprise and Web-Auth captive portal.Cisco WLC مع WPA2-Enterprise وبوابة Web-Auth.
- FortiGate zone policies and guest isolation with AV, IPS and web filtering.سياسات مناطق FortiGate وعزل الضيوف مع مكافحة الفيروسات وIPS وفلترة الويب.
- Layer 2 security with DHCP Snooping and Dynamic ARP Inspection.أمان الطبقة الثانية بـDHCP Snooping وDynamic ARP Inspection.
Want the details behind this project?تريد تفاصيل أكثر عن هذا المشروع؟
I’m happy to walk through the design, the configs and what I would change in production.يسعدني شرح التصميم والإعدادات وما الذي سأغيّره في بيئة الإنتاج.