Hybrid Infrastructure: WS2025 + Azure Arc & Sentinel
An on-premises Windows Server 2025 Domain Controller extended into Azure without migration: onboarded with Azure Arc, monitored through Microsoft Sentinel, and protected by least-privilege networking.Domain Controller محلي بنظام Windows Server 2025 موسَّع إلى Azure دون ترحيل: أُضيف عبر Azure Arc، ويُراقَب بـ Microsoft Sentinel، ومحمي بشبكات بأقل صلاحيات.
Cloud management for a server that stays on-premإدارة سحابية لخادم يبقى محلياً
The Domain Controller (WS2025-DC01) runs on VMware Workstation and stays on-premises. Azure Arc onboards it as a native Azure resource, so it can be managed and monitored from Azure without moving any workload.يعمل الـ Domain Controller (WS2025-DC01) على VMware Workstation ويبقى محلياً. يضيفه Azure Arc كمورد Azure أصلي، فيمكن إدارته ومراقبته من Azure دون نقل أي عبء عمل.
Windows Security Events flow through the Azure Monitor Agent into a Log Analytics workspace and appear in Microsoft Sentinel, where I query them with KQL. The Azure side is kept small: one Resource Group, a VNet with an NSG, and a private Blob container for backups.تمر أحداث أمان Windows عبر Azure Monitor Agent إلى مساحة عمل Log Analytics وتظهر في Microsoft Sentinel، حيث أستعلم عنها بلغة KQL. جانب Azure صغير ومرتب: Resource Group واحدة، وشبكة VNet مع NSG، وحاوية Blob خاصة للنسخ الاحتياطي.
- On-premisesمحلياً
- WS2025-DC01 (Windows Server 2025, VMware Workstation)WS2025-DC01 (Windows Server 2025 على VMware Workstation)
- Hybrid managementالإدارة الهجينة
- Azure Connected Machine Agent, Azure ArcAzure Connected Machine Agent وAzure Arc
- SIEMSIEM
- Azure Monitor Agent, Log Analytics, Microsoft SentinelAzure Monitor Agent وLog Analytics وMicrosoft Sentinel
- Azure networkingشبكات Azure
- VNet + NSG, RDP from a single trusted IP onlyVNet مع NSG، وRDP من عنوان IP موثوق واحد فقط
- Backup targetوجهة النسخ الاحتياطي
- Private Blob container, anonymous access disabledحاوية Blob خاصة، والوصول المجهول معطّل
How the pieces connectكيف ترتبط الأجزاء
- WS2025-DC01 runs on-premises under VMware.WS2025-DC01 يعمل محلياً على VMware.
- The Azure Connected Machine Agent registers it with Azure Arc.يسجّله Azure Connected Machine Agent في Azure Arc.
- Windows Security Events are collected by the Azure Monitor Agent.يجمع Azure Monitor Agent أحداث أمان Windows.
- Events land in Log Analytics and are analysed in Microsoft Sentinel.تصل الأحداث إلى Log Analytics وتُحلَّل في Microsoft Sentinel.
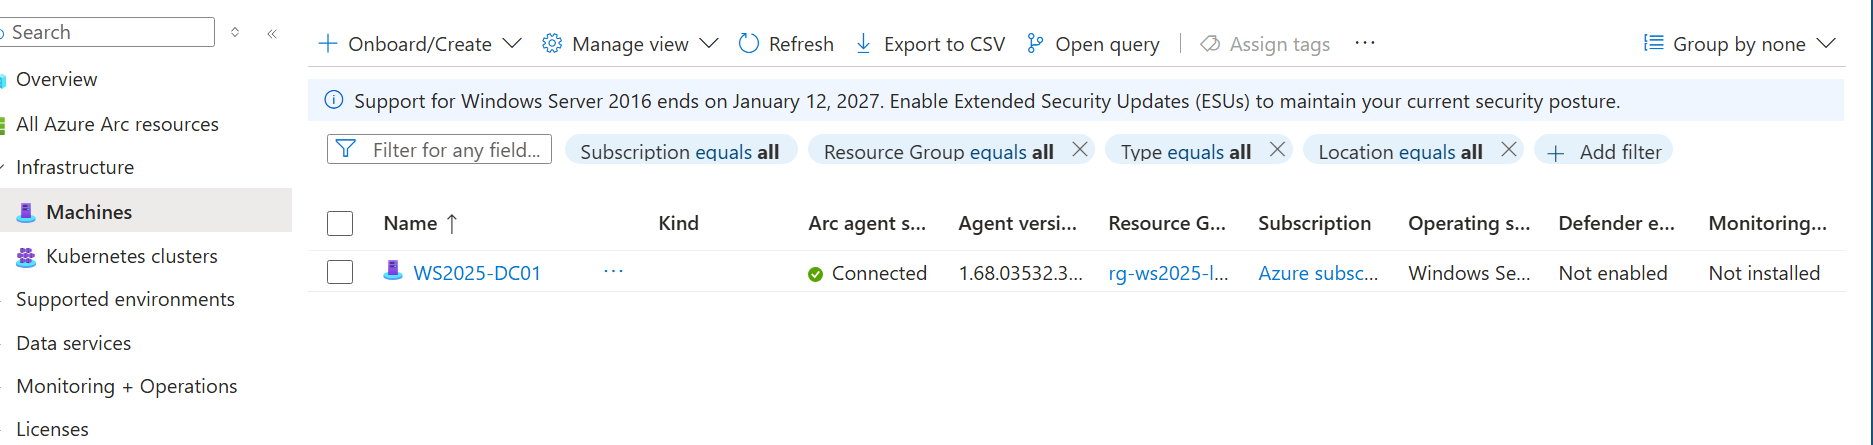
Azure Arc: the DC as an Azure resourceAzure Arc: الـ DC كمورد في Azure
Arc shows the on-prem Domain Controller in the Connected state, so it is managed from the Azure portal like any other resource.يعرض Arc الـ Domain Controller المحلي بحالة Connected، فيُدار من بوابة Azure مثل أي مورد آخر.
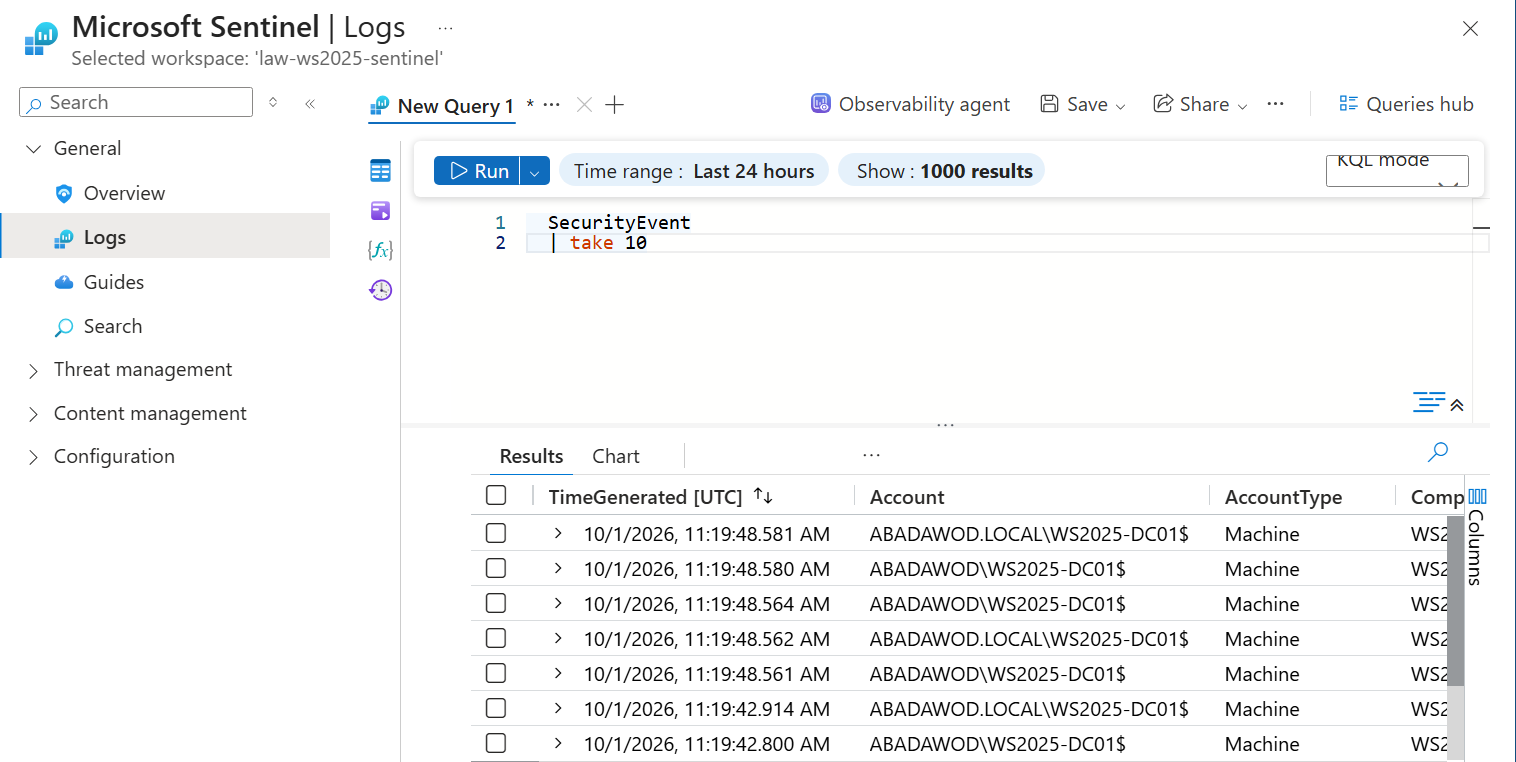
Microsoft Sentinel and KQLMicrosoft Sentinel وKQL
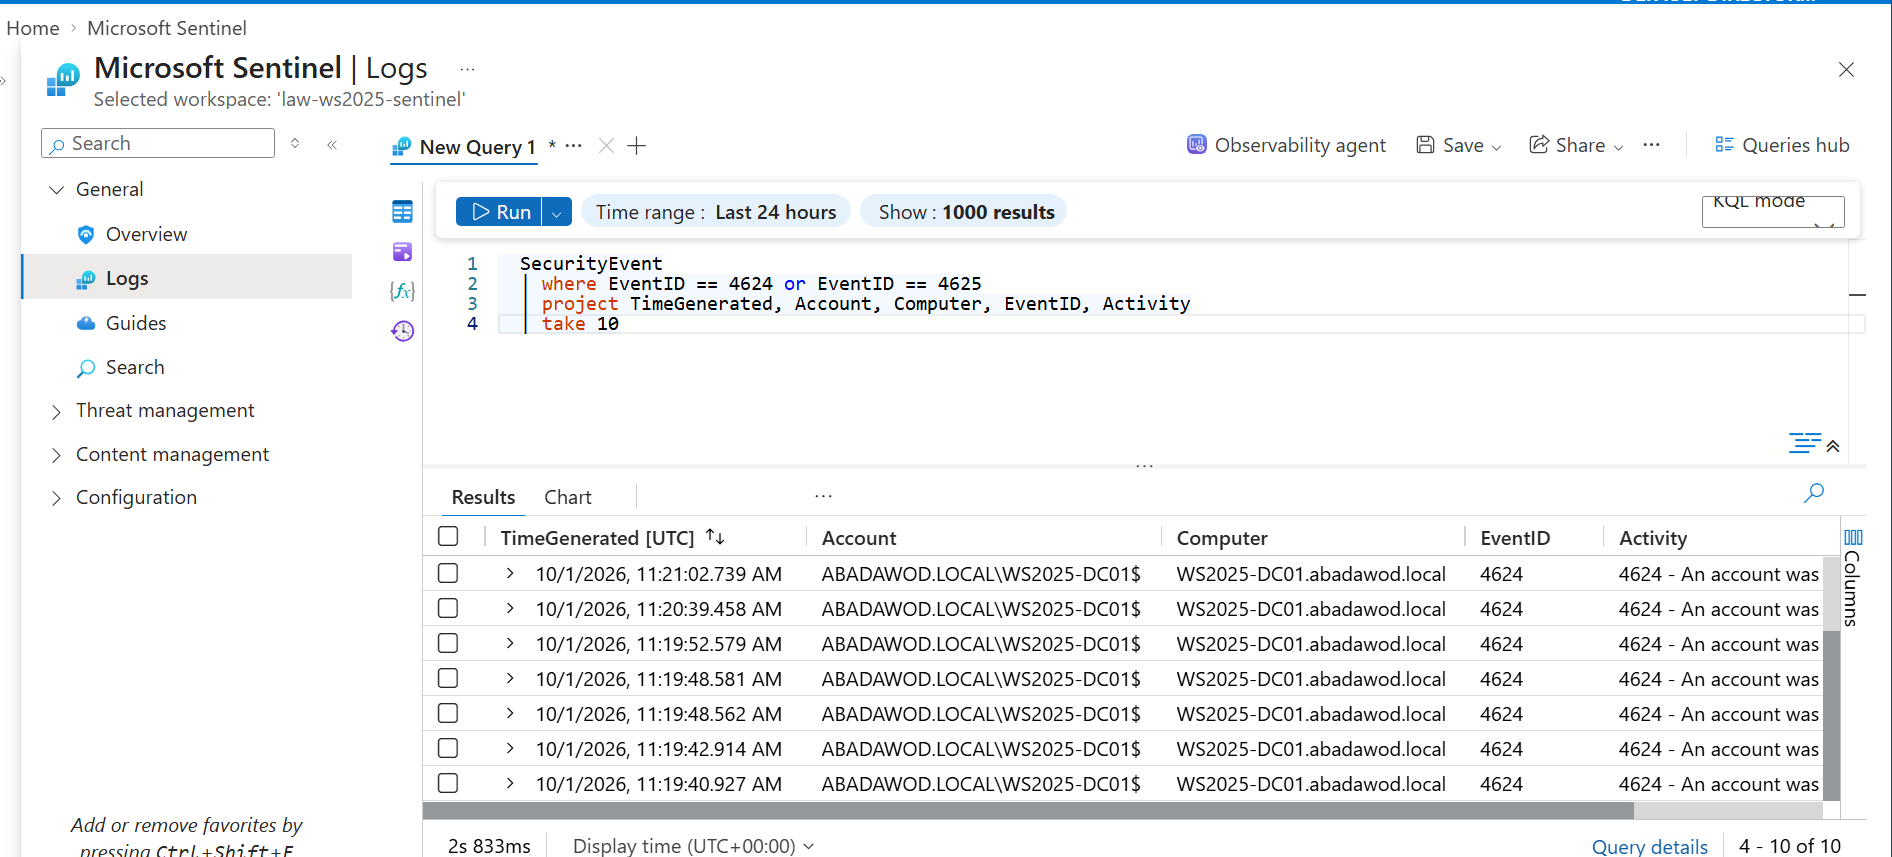
I confirmed that live SecurityEvent data reaches Sentinel, then filtered it for logon events (Event IDs 4624 and 4625).تأكدت أن بيانات SecurityEvent المباشرة تصل إلى Sentinel، ثم صفّيتها لأحداث تسجيل الدخول (Event ID 4624 و4625).
- Query: SecurityEvent | where EventID == 4624 or EventID == 4625 | project TimeGenerated, Account, Computer, EventID, Activity | take 10الاستعلام: SecurityEvent | where EventID == 4624 or EventID == 4625 | project TimeGenerated, Account, Computer, EventID, Activity | take 10
Least-privilege networkingشبكات بأقل صلاحيات
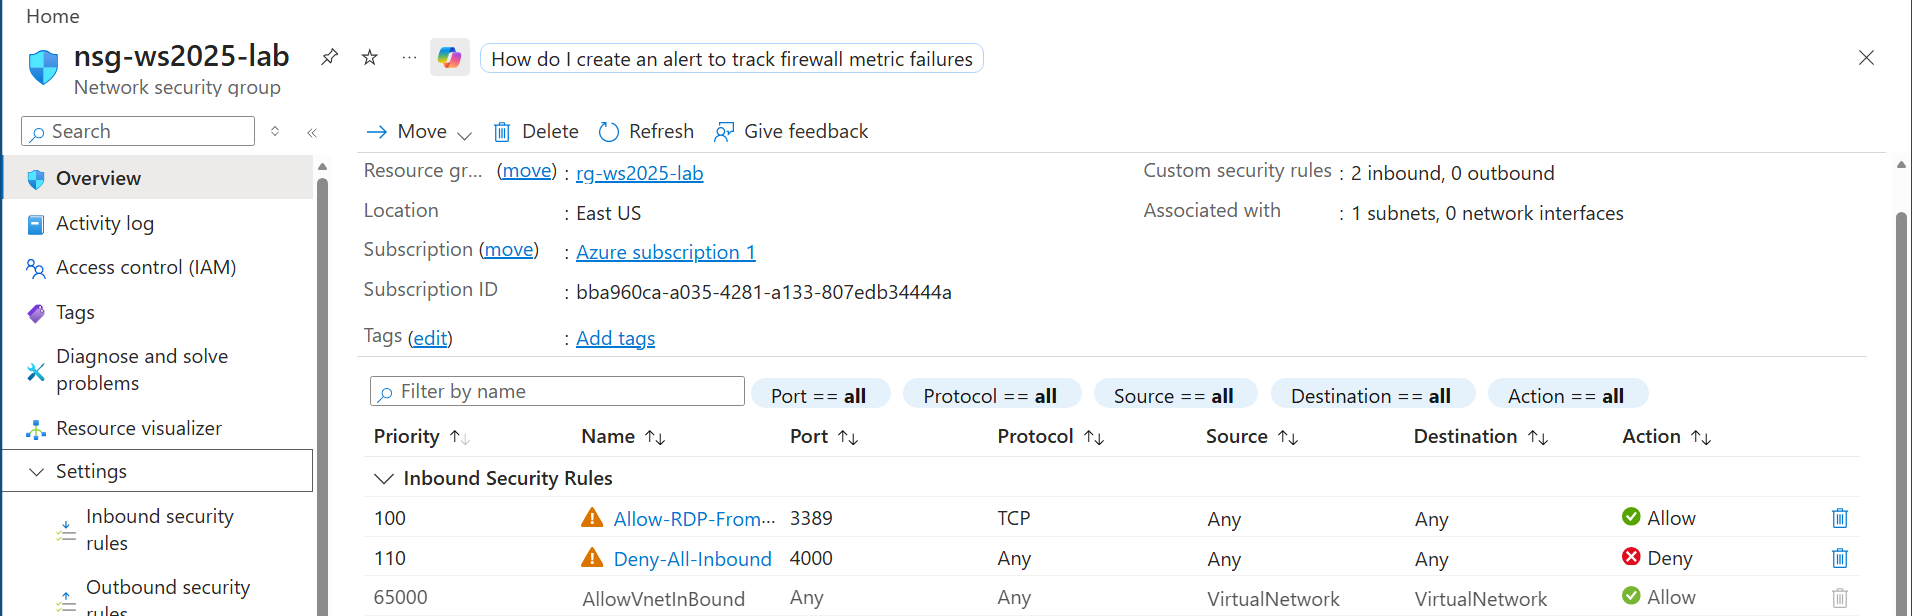
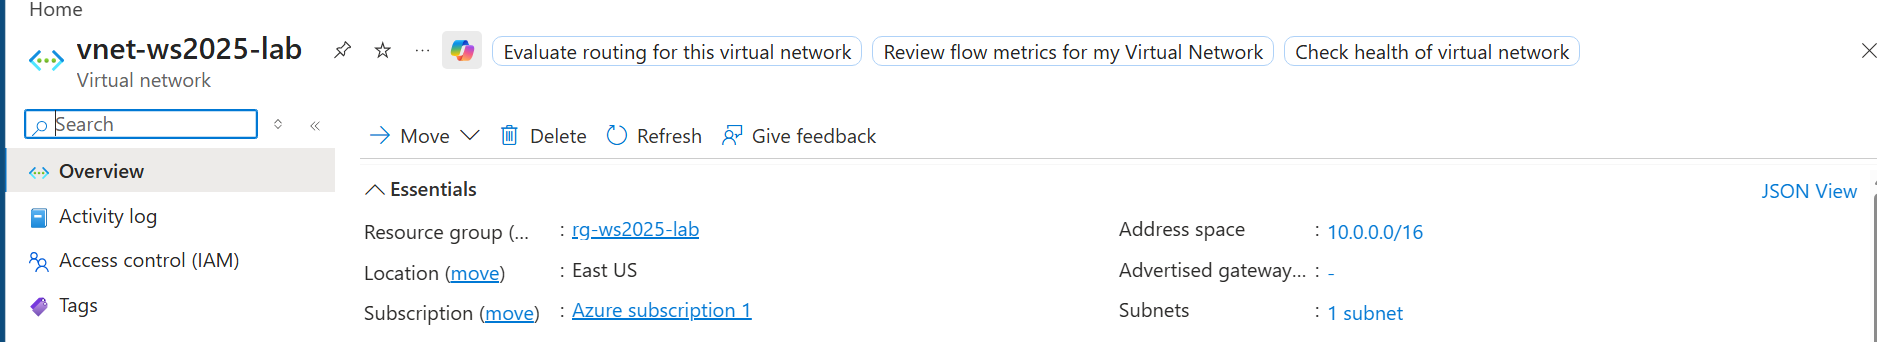
- A dedicated VNet and NSG back the Azure side.يدعم جانب Azure شبكة VNet وNSG مخصصة.
- The NSG has one inbound allow rule for RDP from a single trusted IP, and an explicit deny-all for everything else.في الـ NSG قاعدة واردة واحدة تسمح بـ RDP من عنوان IP موثوق واحد، وقاعدة منع الكل صريحة لما سواه.
Backup target and resource layoutوجهة النسخ الاحتياطي وتنظيم الموارد
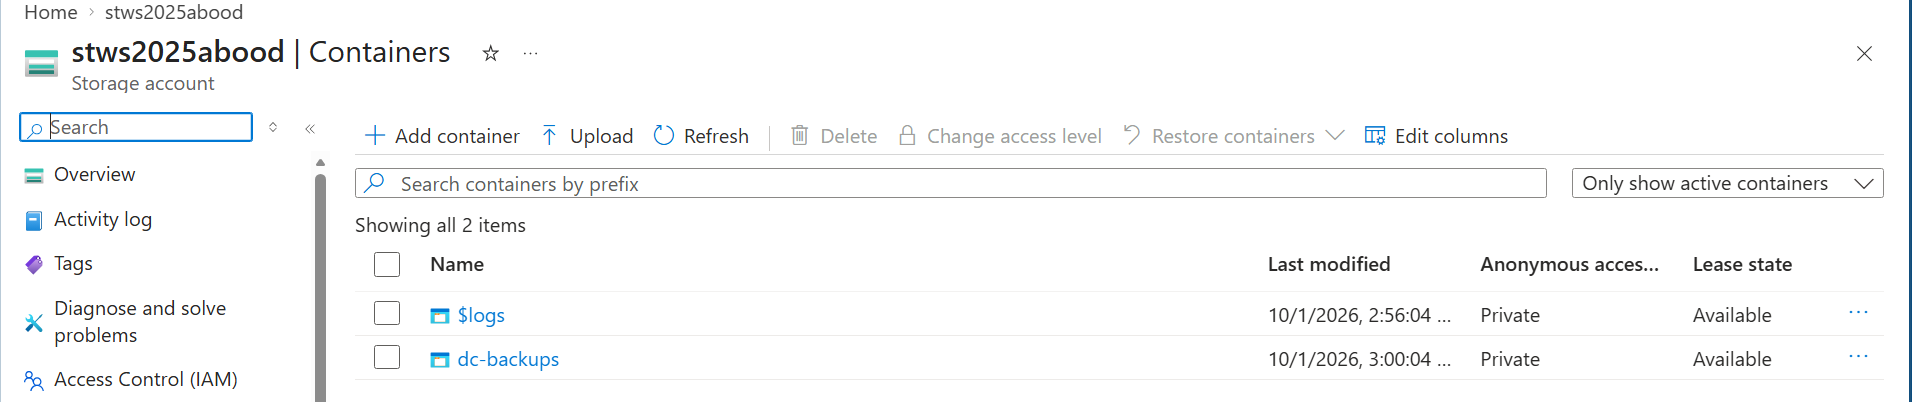
- A private Blob container with anonymous access disabled is the backup destination.وجهة النسخ الاحتياطي حاوية Blob خاصة والوصول المجهول فيها معطّل.
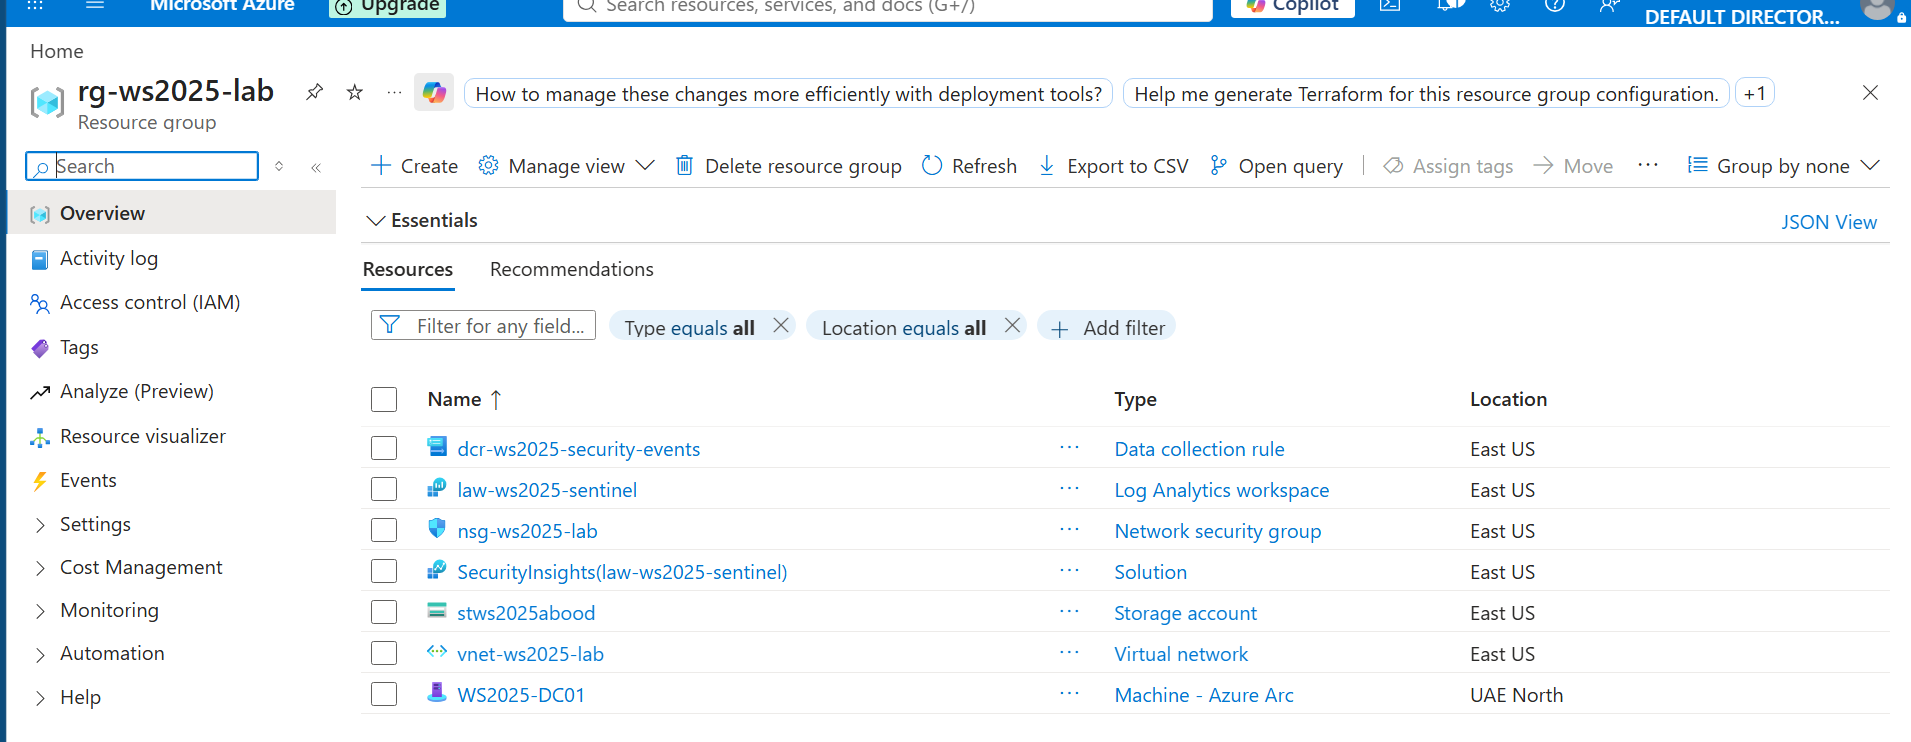
- Every resource sits under a single Resource Group.كل الموارد تحت Resource Group واحدة.
What went wrong, and the fixوش اللي تعطّل، وكيف انحلّ
- Firewall rule stopped working after promotion. A Windows Firewall rule scoped to the Private profile silently stopped applying once the server became a Domain Controller, because its active profile switched to Domain.قاعدة الجدار الناري توقفت بعد الترقية. قاعدة في Windows Firewall مخصصة لملف Private توقفت عن العمل بصمت بعد ما صار الخادم Domain Controller، لأن الملف النشط تحوّل إلى Domain.
- Storage Account in the wrong region. Every other resource was in East US, but the region field had defaulted and I did not double-check it. I deleted the account and recreated it in the right region.حساب التخزين في منطقة غلط. كل الموارد في East US، لكن حقل المنطقة اتعبّى تلقائياً وما راجعته. حذفت الحساب وأعدت إنشاءه في المنطقة الصحيحة.
- Azure sign-up failed with state_mismatch. Several browser tabs open during account creation desynchronised the sign-in state. I closed them all and restarted sign-up in a single session.فشل التسجيل في Azure بخطأ state_mismatch. فتح عدة تبويبات أثناء إنشاء الحساب أفسد حالة تسجيل الدخول. قفلتها كلها وأعدت التسجيل في جلسة واحدة.
What this project showsما يُظهره هذا المشروع
- Onboarding on-prem servers to Azure with Azure Arc.إضافة الخوادم المحلية إلى Azure عبر Azure Arc.
- Sending Windows Security Events to Microsoft Sentinel and querying them with KQL.إرسال أحداث أمان Windows إلى Microsoft Sentinel والاستعلام عنها بـ KQL.
- Applying least-privilege rules with NSGs.تطبيق قواعد أقل صلاحيات بـ NSG.
- Securing a backup target on Azure Blob Storage.تأمين وجهة نسخ احتياطي على Azure Blob Storage.
- Extending AZ-104 topics (monitoring, virtual networking) into hybrid management.توسيع مواضيع AZ-104 (المراقبة والشبكات الافتراضية) إلى الإدارة الهجينة.
Want the details behind this project?تريد تفاصيل أكثر عن هذا المشروع؟
I’m happy to walk through the design, the configs and what I would change in production.يسعدني شرح التصميم والإعدادات وما الذي سأغيّره في بيئة الإنتاج.