CyberKey — Hardware Incident Response
A physical key built on an ATtiny85 microcontroller that triggers network isolation and a domain account lockout in one automated workflow.مفتاح مادي مبني على المتحكم ATtiny85 يطلق عزل الشبكة وقفل حساب النطاق في سير عمل آلي واحد.
Incident response you can trigger by handاستجابة للحوادث تُطلقها بيدك
CyberKey connects a small piece of hardware to enterprise security infrastructure. When it is activated, the device starts a chain that isolates a FortiGate interface through its API and locks the targeted account on the Domain Controller.يربط CyberKey قطعة عتاد صغيرة ببنية الأمن المؤسسية. عند تفعيله يبدأ الجهاز سلسلة تعزل واجهة FortiGate عبر API وتقفل الحساب المستهدف على متحكم النطاق.
The idea is to contain an incident with a single physical action.الفكرة هي احتواء الحادث بإجراء مادي واحد.
- Hardwareالعتاد
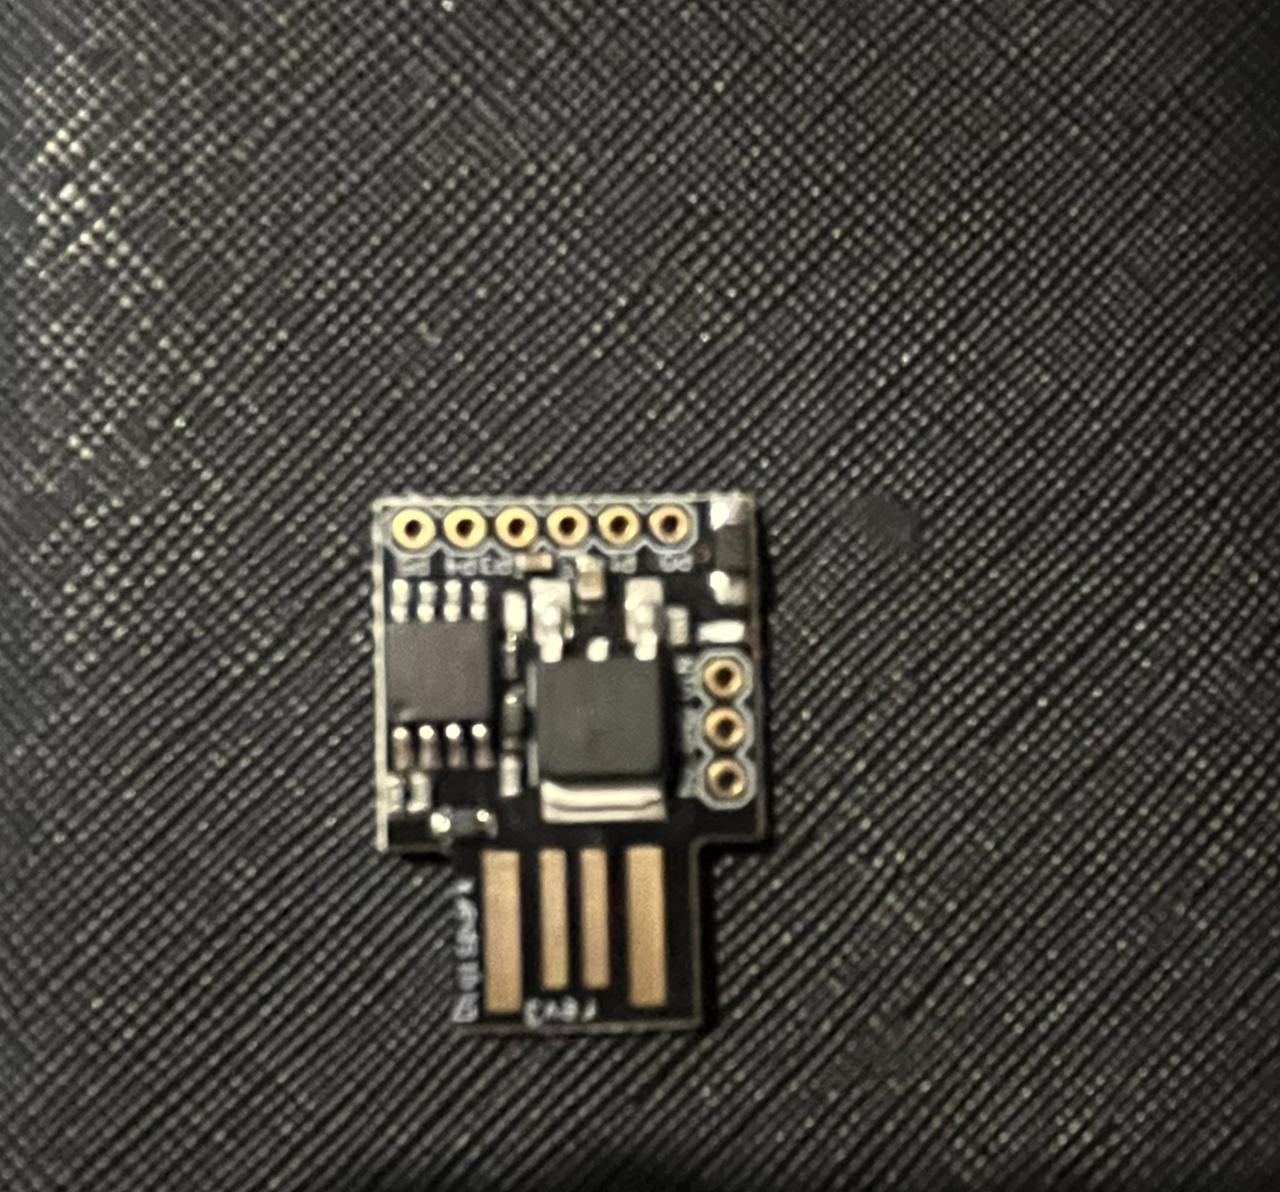
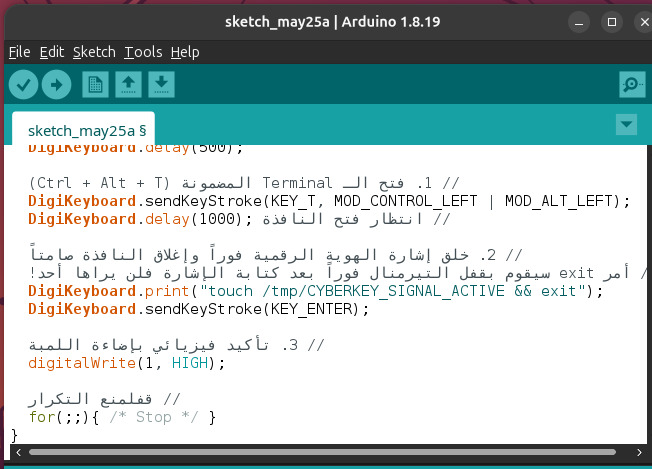
- ATtiny85 (Digispark), programmed in Arduino IDEATtiny85 (Digispark)، يُبرمج عبر Arduino IDE
- Backendالخلفية
- Python socket communication (port 9999) and Bash scriptingاتصال Python socket (المنفذ 9999) وسكربتات Bash
- Integrationsالتكاملات
- FortiGate API and Active DirectoryFortiGate API وActive Directory
- Operating systemنظام التشغيل
- Ubuntu LinuxUbuntu Linux
How it worksكيف يعمل
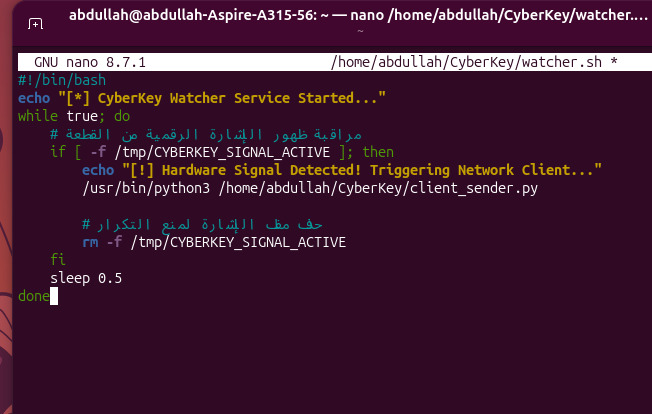
- Trigger. Activating the ATtiny85 device writes a signal file.التفعيل. تشغيل جهاز ATtiny85 يكتب ملف إشارة.
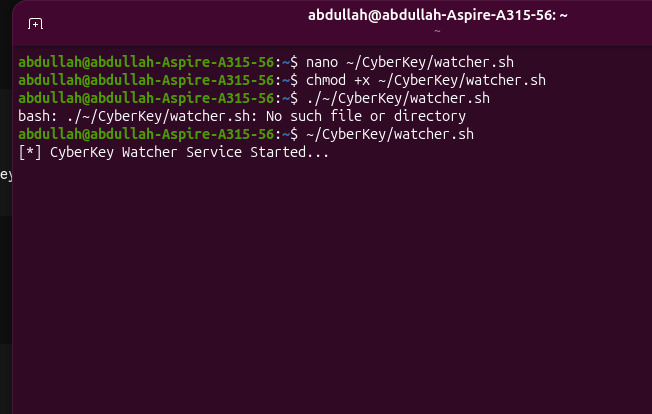
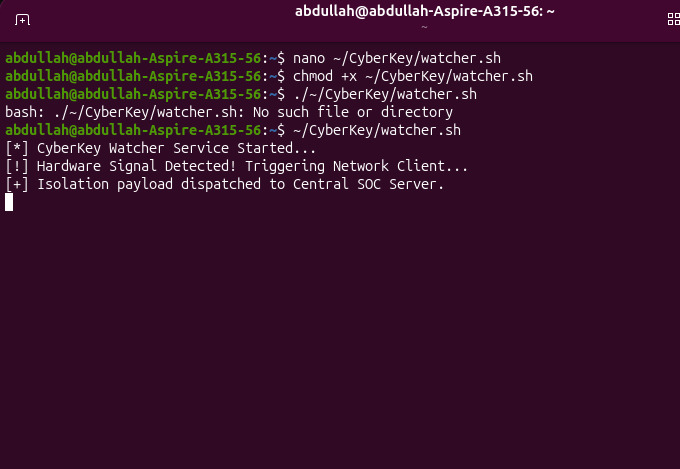
- Watch. A Bash service monitors for that signal file.المراقبة. خدمة Bash تراقب ظهور ملف الإشارة.
- Notify. The Bash service starts a Python network client, which talks to the SOC server on port 9999.الإبلاغ. تشغّل خدمة Bash عميل شبكة بلغة Python يتصل بخادم SOC على المنفذ 9999.
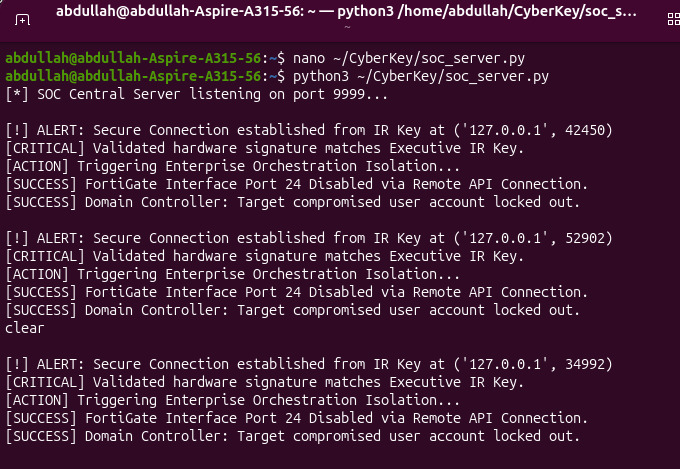
- Isolate. The SOC server calls the FortiGate API to isolate the interface.العزل. يستدعي خادم SOC واجهة FortiGate API لعزل الواجهة.
- Lock. The SOC server locks the account on the Domain Controller through Active Directory.القفل. يقفل خادم SOC الحساب على متحكم النطاق عبر Active Directory.
The device and setupالجهاز والإعداد
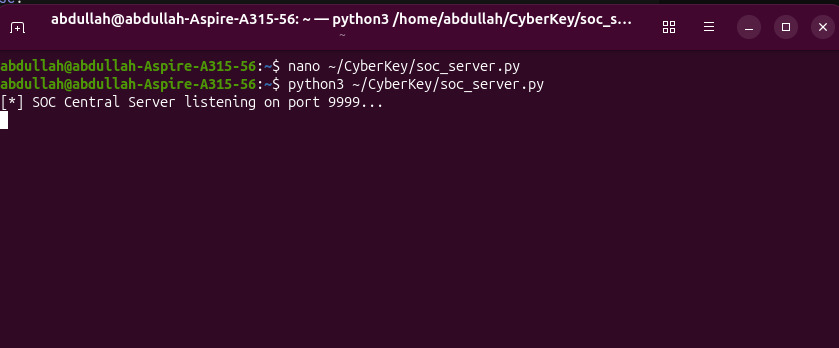
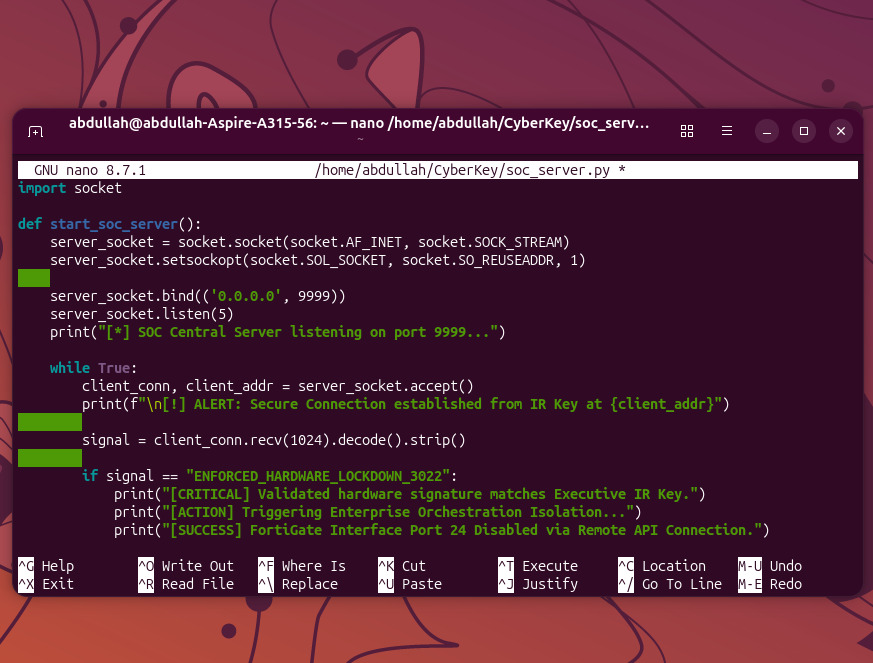
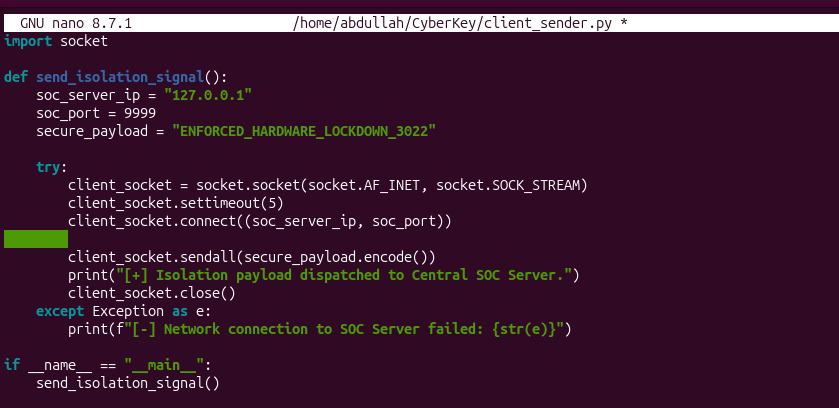
The response in actionالاستجابة أثناء العمل
What this project showsما يُظهره هذا المشروع
- Connecting hardware, scripts and enterprise systems into one workflow.ربط العتاد والسكربتات والأنظمة المؤسسية في سير عمل واحد.
- Using the FortiGate API for automated containment.استخدام FortiGate API للاحتواء الآلي.
- Automating Active Directory account actions.أتمتة إجراءات حسابات Active Directory.
- Designing a simple client-server protocol in Python.تصميم بروتوكول بسيط بين عميل وخادم بلغة Python.
Want the details behind this project?تريد تفاصيل أكثر عن هذا المشروع؟
I’m happy to walk through the design, the configs and what I would change in production.يسعدني شرح التصميم والإعدادات وما الذي سأغيّره في بيئة الإنتاج.