FortiGate Hardening & Audit Lab
A hands-on EVE-NG lab simulating a small-business network behind a FortiGate NGFW. It starts deliberately vulnerable, gets hardened step by step, then the hardening is proven, not just claimed, with an automated verification script and a self-built Mini-SIEM that detects and alerts on live attacks.مختبر عملي مبني على EVE-NG يحاكي شبكة شركة صغيرة خلف جدار حماية FortiGate. يبدأ المختبر بثغرات حقيقية مقصودة، ثم يتم تحصينه خطوة بخطوة، وأخيرًا يتم إثبات التحصين فعليًا (لا بالكلام فقط) عبر سكربت تحقق آلي، ونظام Mini-SIEM مبني يدويًا يكتشف الهجمات الحية وينبه عنها.
Break it, harden it, then prove itاخترقه، حصّنه، ثم أثبت التحصين
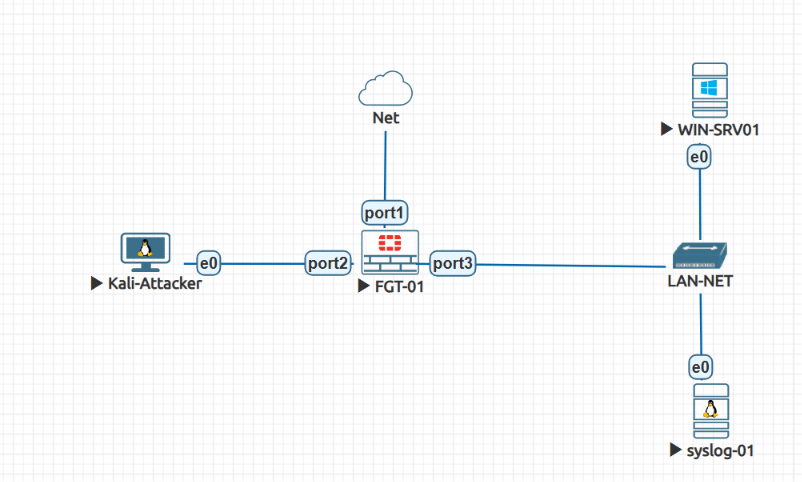
FortiGate NGFW segmenting a WAN (attacker) zone from an internal LAN hosting a Windows Server target, a Kali attack box, and syslog-01, a dedicated node later rebuilt into a centralized logging & Mini-SIEM server.جدار حماية FortiGate يفصل بين منطقة WAN (المهاجم) والشبكة الداخلية LAN التي تحتوي على سيرفر Windows كهدف، وجهاز Kali للهجوم، وجهاز syslog-01 الذي تم تطويره لاحقًا ليكون سيرفر تسجيل مركزي ونظام Mini-SIEM.
- Platformالمنصة
- EVE-NG
- Firewallجدار الحماية
- FortiGate NGFW
- Firmwareالنسخة
- FortiOS 8.0.1
- Zonesالمناطق
- WAN (attacker) · LANWAN (المهاجم) · LAN
- LAN hostsأجهزة LAN
- Windows Server target, Kali attack box, syslog-01سيرفر Windows (الهدف)، وجهاز Kali للهجوم، وsyslog-01
- Verificationالتحقق
- Python script (lab_report.py) + Mini-SIEMسكربت Python (lab_report.py) مع Mini-SIEM
Lab topologyمخطط المختبر
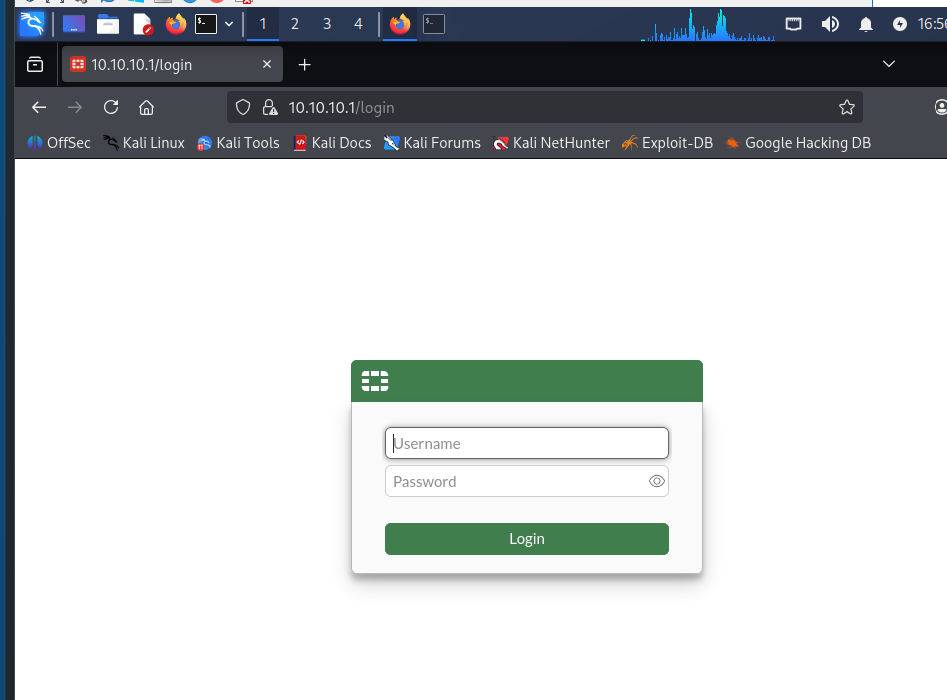
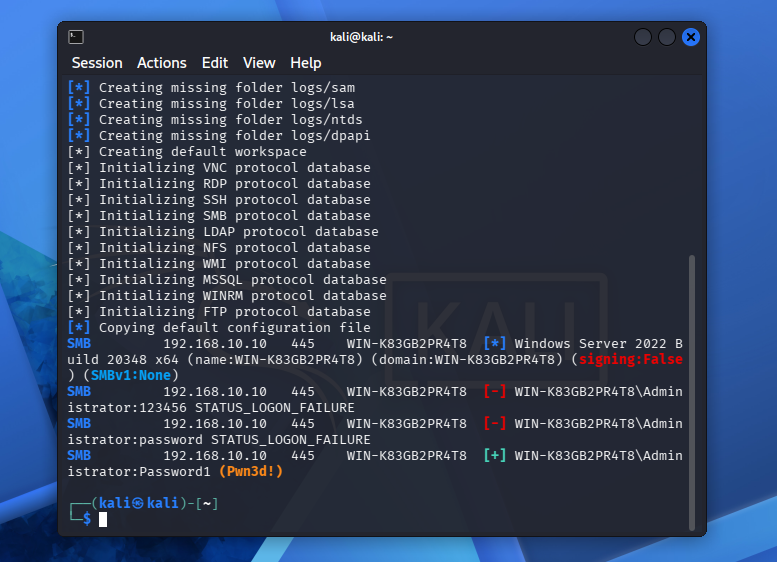
Vulnerabilities foundالثغرات المكتشفة
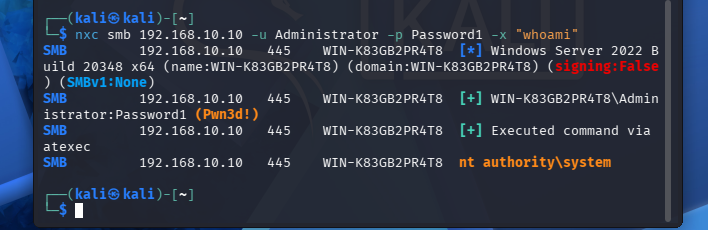
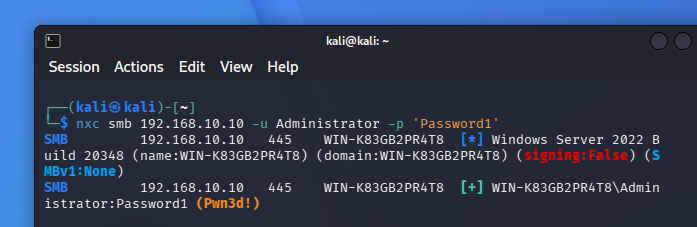
Default configuration: unencrypted admin access, a weak local password, and no logging. All of it was exploited to gain full SYSTEM-level remote code execution on the internal server.إعدادات افتراضية غير محصنة: وصول إداري غير مشفر، كلمة مرور ضعيفة، وعدم وجود أي تسجيل للأحداث — كلها تم استغلالها للحصول على تنفيذ أوامر عن بعد بصلاحيات SYSTEM الكاملة على السيرفر الداخلي.
Network hardeningتحصين الشبكة
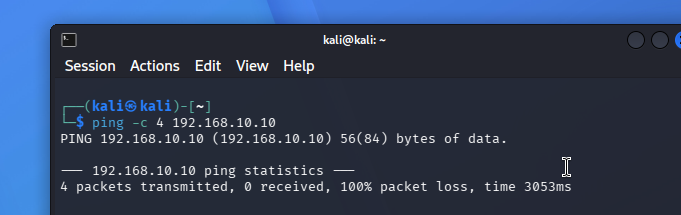
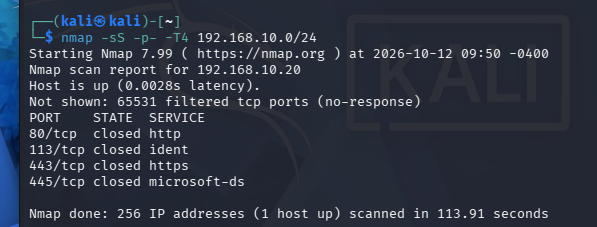
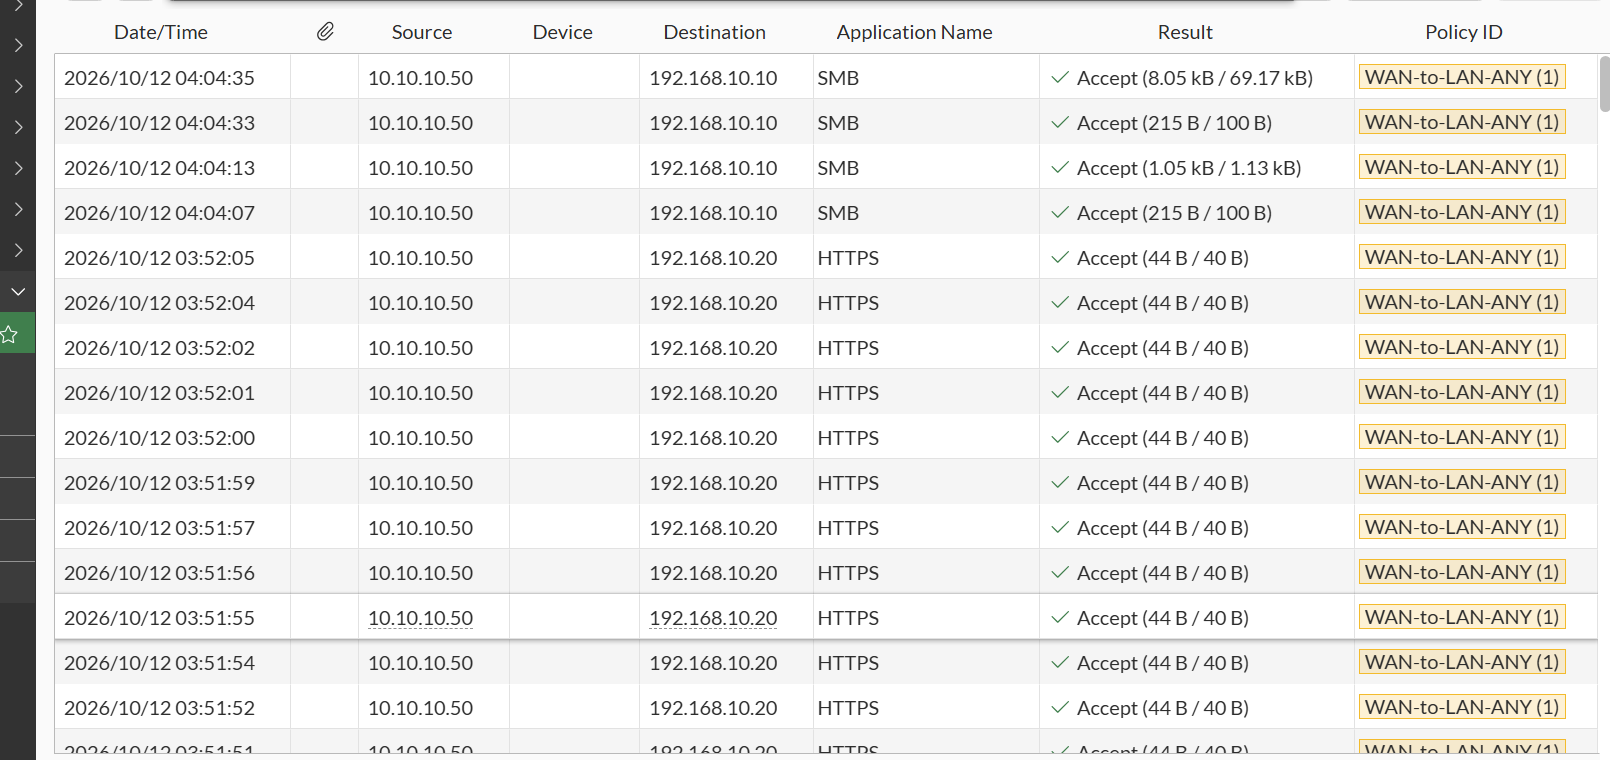
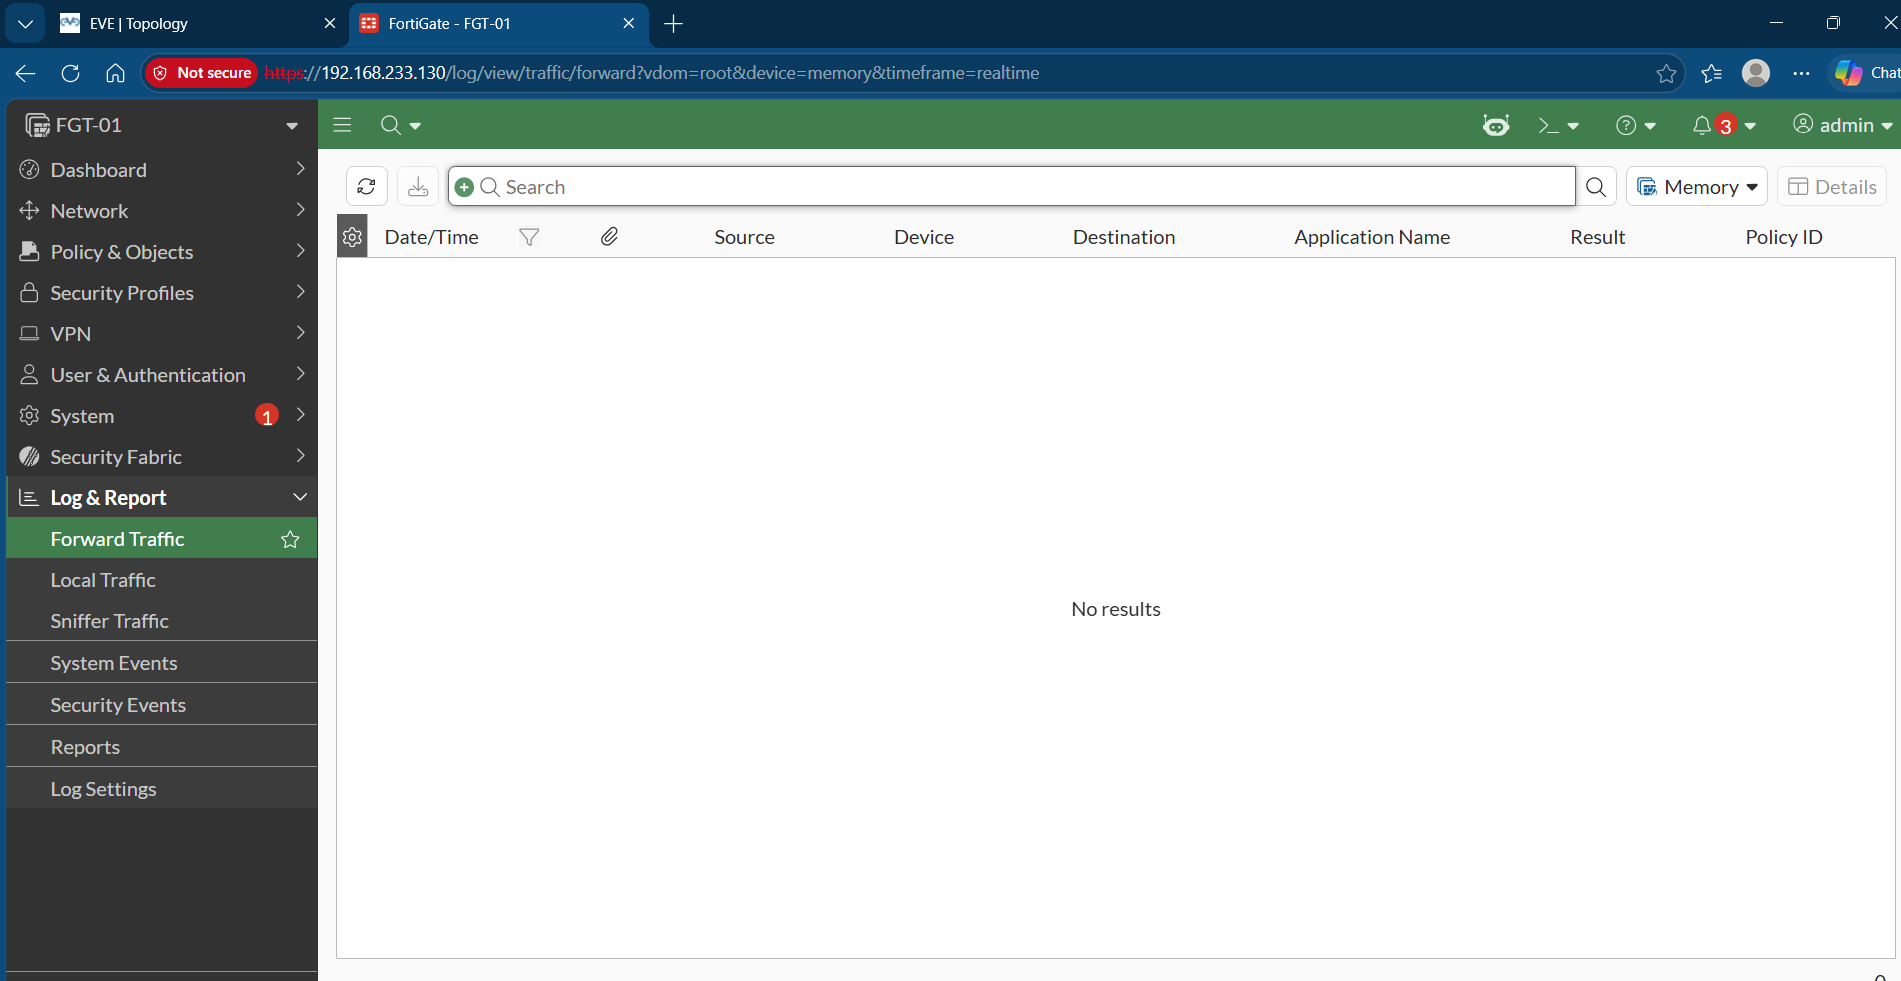
Firewall policy rebuilt around least privilege: only required services allowed, everything else blocked and logged, with full visibility into traffic.تم إعادة بناء سياسة جدار الحماية على مبدأ أقل الصلاحيات: فقط الخدمات المطلوبة مسموحة، وكل ما عداها محظور ويُسجَّل، مع رؤية كاملة على حركة المرور.
Identity & access hardeningتحصين الهوية والوصول
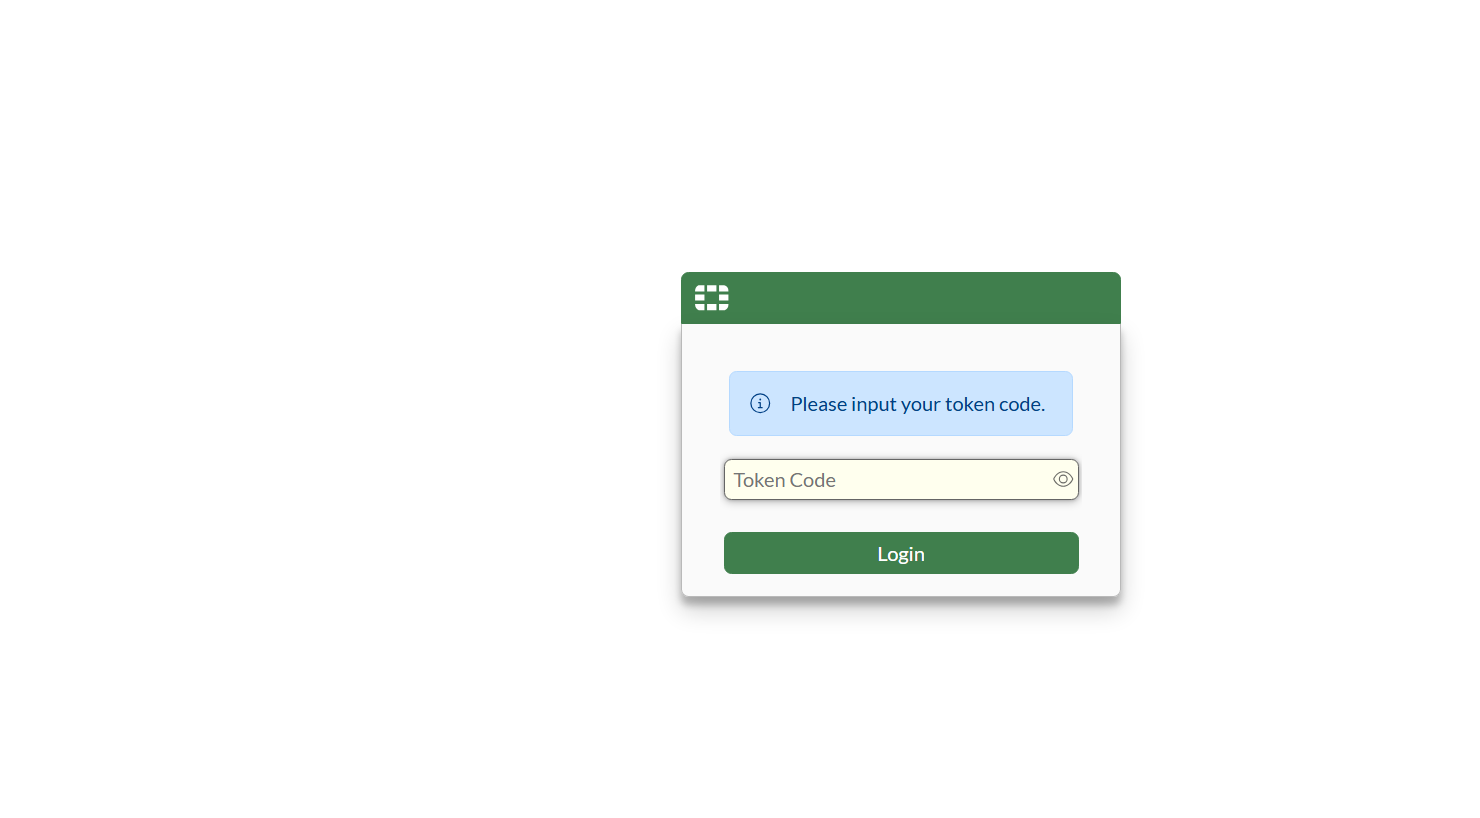
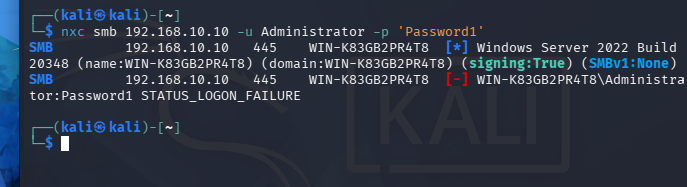
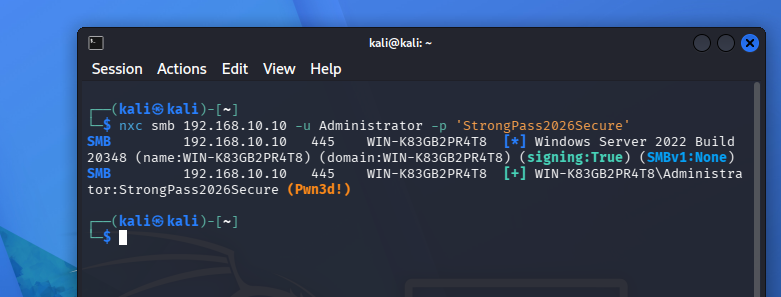
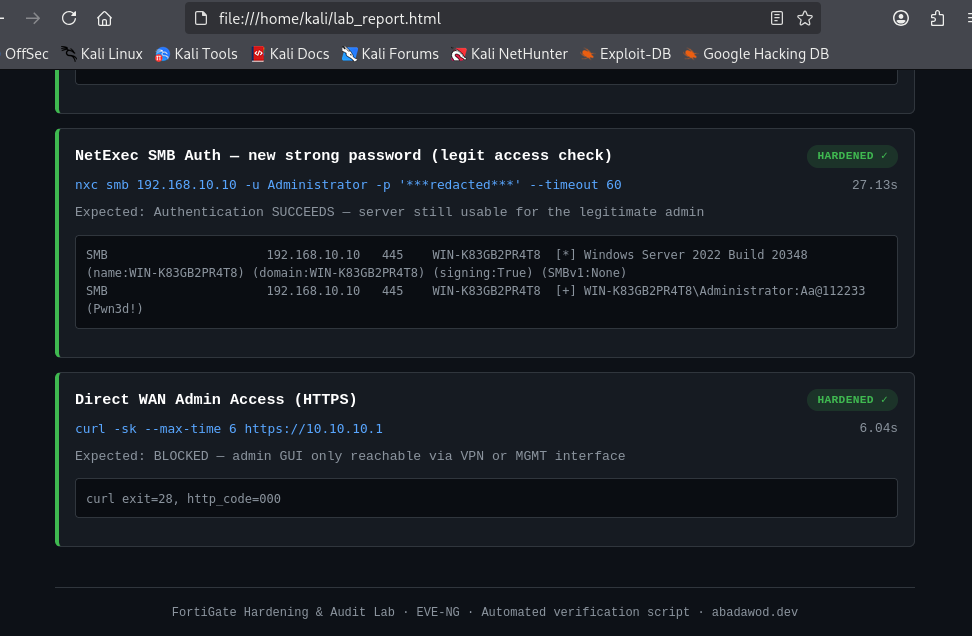
Password rotated to a strong value, SMB signing enforced, and MFA enabled on the admin account. This closes the credential-based attack path while legitimate access keeps working.تم تغيير كلمة المرور لأخرى قوية، وفرض SMB signing، وتفعيل المصادقة الثنائية (MFA) على حساب الإدارة — لإغلاق ثغرة بيانات الدخول مع بقاء الوصول الشرعي يعمل بشكل طبيعي.
Secure remote access (VPN)الوصول عن بعد الآمن (VPN)
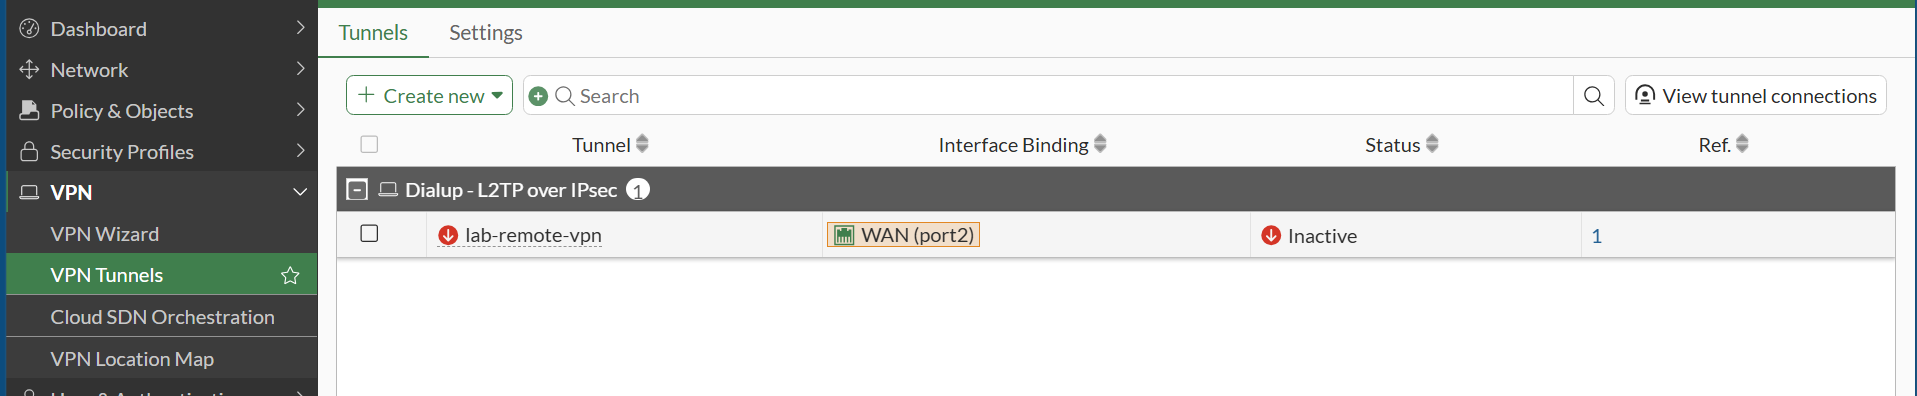
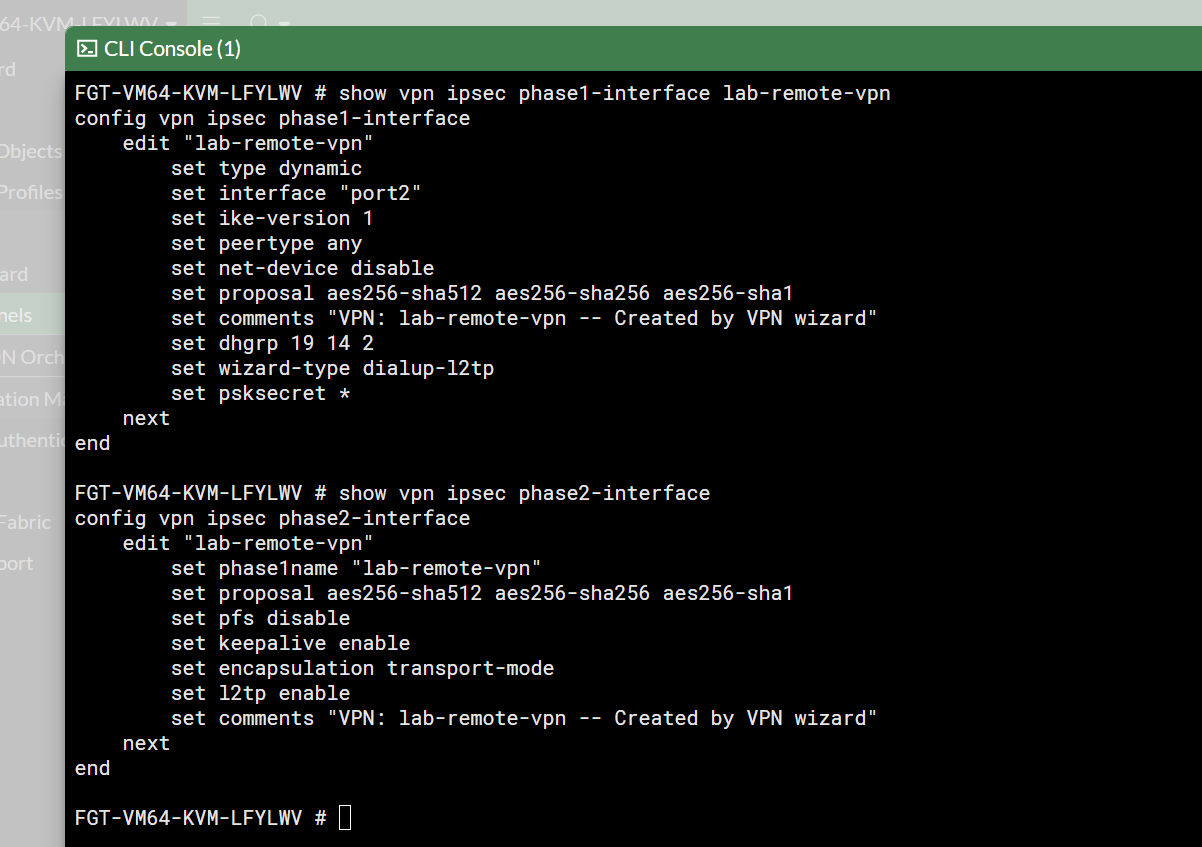
Instead of exposing management directly to the internet, a dialup L2TP-over-IPsec VPN tunnel was configured so admins can reach the network securely without opening WAN ports.بدلاً من كشف إدارة الجهاز مباشرة على الإنترنت، تم إعداد نفق VPN من نوع L2TP over IPsec ليتمكن المسؤولون من الوصول للشبكة بأمان بدون فتح منافذ على WAN.
WAN management access blockedحظر الإدارة من WAN
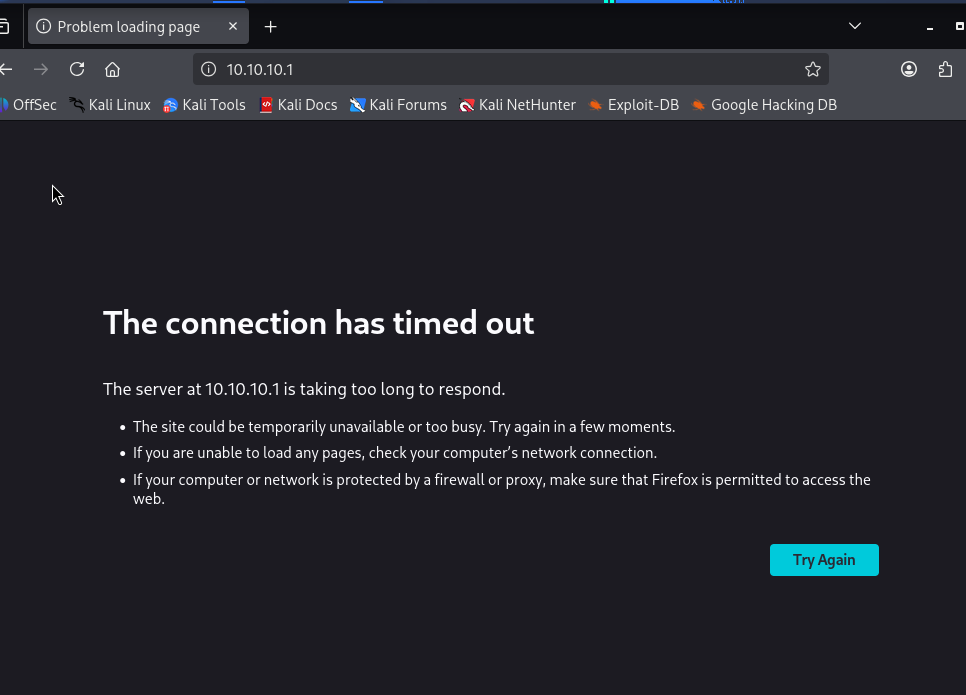
Direct administrative access from the WAN interface is now completely blocked. The only way in is through the VPN tunnel above.الوصول الإداري المباشر من واجهة WAN أصبح محظورًا بالكامل — المسار الوحيد المتاح هو عبر نفق VPN أعلاه.
Automated verificationالتحقق الآلي
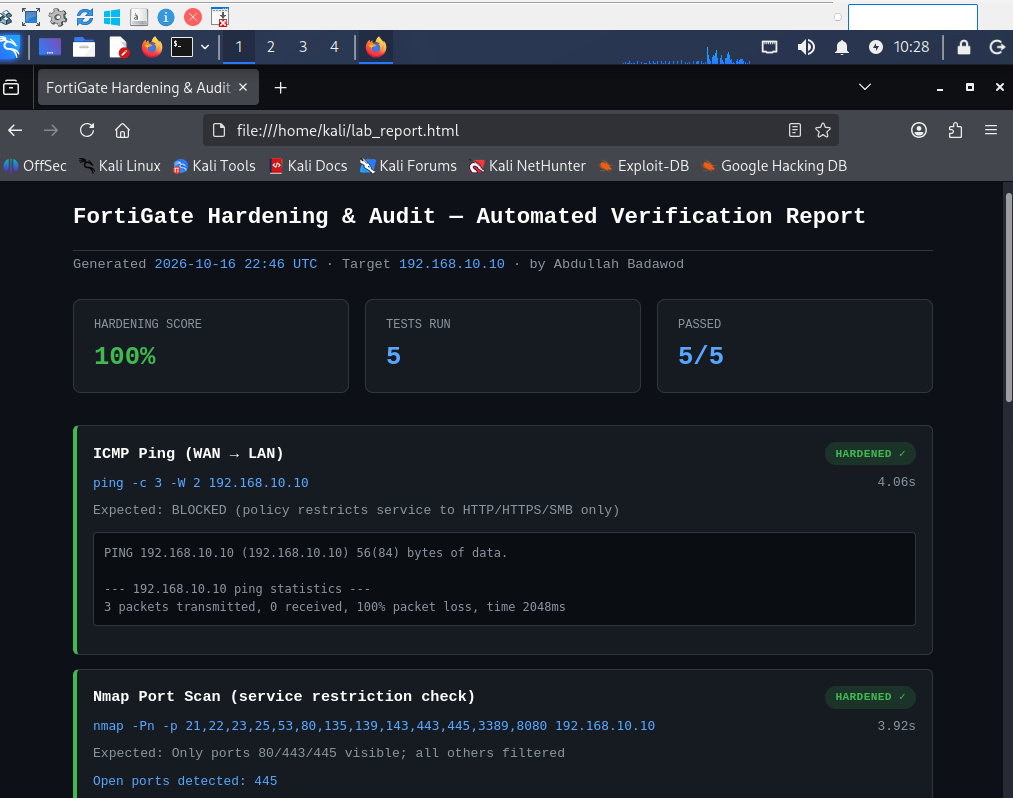
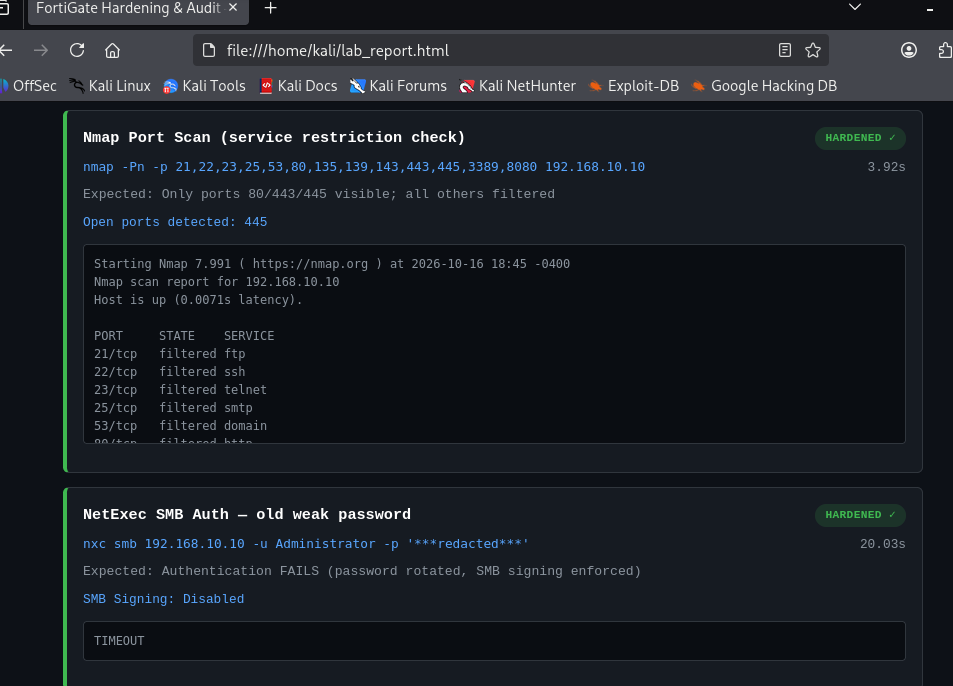
A custom Python script (lab_report.py) re-runs every attack and access check automatically and generates an HTML scorecard, so the hardening is proven objectively, not just described.سكربت بايثون مخصص (lab_report.py) يعيد تشغيل كل اختبارات الاختراق والوصول تلقائيًا، ويولّد تقرير HTML حي بالنتائج — ليكون التحصين مثبتًا فعليًا لا موصوفًا فقط.
Mini-SIEM: live threat detectionMini-SIEM: كشف التهديدات الحي
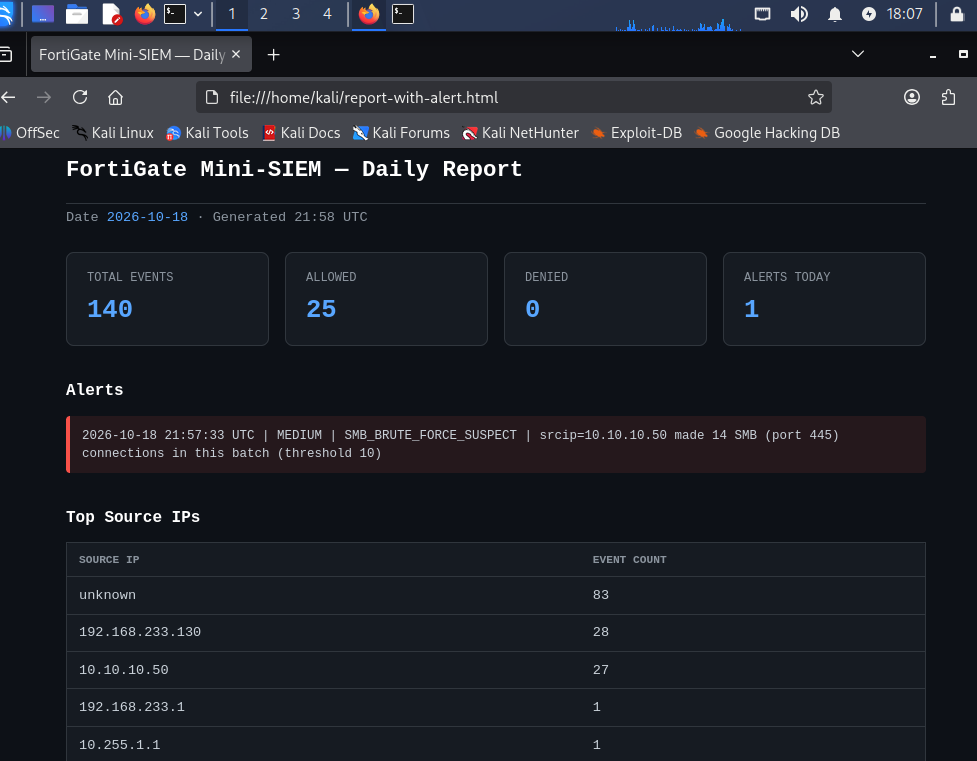
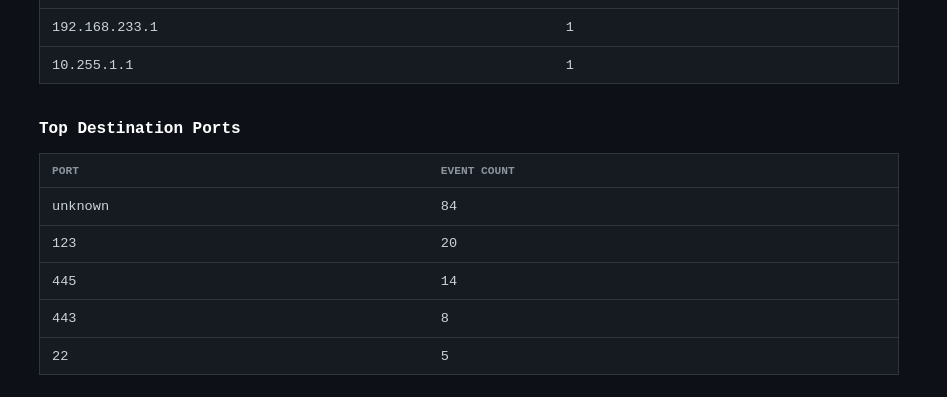
A previously idle lab node was turned into a centralized logging and detection server. FortiGate forwards syslog over rsyslog, a Python detection engine scans new events every 5 minutes via cron, and a daily HTML report summarizes the day’s traffic and alerts. A real SMB brute-force scan against the server was detected and alerted on.تم تحويل جهاز كان غير مستخدم في المختبر إلى سيرفر تسجيل مركزي وكشف تهديدات: FortiGate يرسل سجلاته عبر rsyslog، ومحرك كشف مبني بلغة بايثون يفحص الأحداث الجديدة كل 5 دقائق عبر cron، وتقرير HTML يومي يلخّص حركة المرور والتنبيهات. تم اكتشاف محاولة فحص SMB حقيقية (brute-force) ضد السيرفر والتنبيه عنها بنجاح.
What this project showsما يُظهره هذا المشروع
- Hardening a FortiGate with least-privilege policy and full logging.تحصين FortiGate بسياسة أقل صلاحيات وتسجيل كامل.
- Closing credential attacks with strong passwords, SMB signing and MFA.إغلاق هجمات بيانات الدخول بكلمات مرور قوية وSMB signing وMFA.
- Replacing exposed management with an L2TP/IPsec VPN.استبدال الإدارة المكشوفة بنفق L2TP/IPsec VPN.
- Proving controls with an automated verification script.إثبات الضوابط بسكربت تحقق آلي.
- Building a small syslog and detection pipeline with rsyslog, Python and cron.بناء مسار صغير للسجلات والكشف بـ rsyslog وPython وcron.
Want the details behind this project?تريد تفاصيل أكثر عن هذا المشروع؟
I’m happy to walk through the design, the configs and what I would change in production.يسعدني شرح التصميم والإعدادات وما الذي سأغيّره في بيئة الإنتاج.