Mini SOC Platform: Custom Threat Detection + Wazuh
A security monitoring platform that merges two alert sources, my own Apache log detection and Wazuh endpoint telemetry, into one database, with IP reputation checks and Telegram alerts.منصة مراقبة أمنية تدمج مصدرَي تنبيهات في قاعدة بيانات واحدة: كشفي الخاص على سجلات Apache وبيانات Wazuh من الأجهزة، مع فحص سمعة IP وتنبيهات Telegram.
Two alert streams, one timelineمساران للتنبيهات، وخط زمني واحد
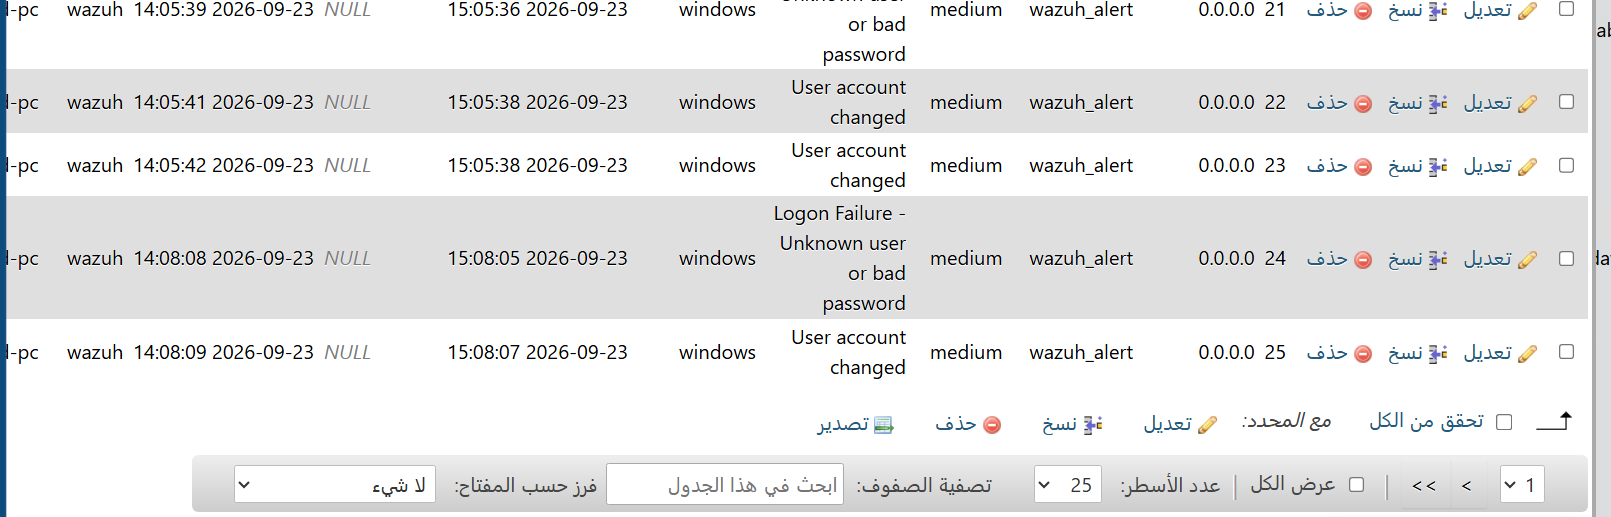
Apache access logs go through custom PHP detection rules, and Windows endpoint events come from a Wazuh agent. Both land in the same threat_events table, so web attacks and endpoint events can be read side by side.تمر سجلات Apache عبر قواعد كشف PHP مخصصة، وتأتي أحداث أجهزة Windows من عميل Wazuh. وتصل كلها إلى جدول threat_events نفسه، فتُقرأ هجمات الويب وأحداث الأجهزة جنباً إلى جنب.
Events are enriched with an AbuseIPDB reputation check, high-severity ones are pushed to Telegram, and a weekly report covers both sources.تُغنى الأحداث بفحص سمعة من AbuseIPDB، وتُرسل العالية الخطورة إلى Telegram، ويغطي تقرير أسبوعي المصدرين.
The Apache side runs on live traffic: it has analysed 10,255 requests from 1,667 unique IPs.جانب Apache يعمل على مرور حقيقي: حلّل 10,255 طلباً من 1,667 عنوان IP فريداً.
- Stream 1المسار 1
- Apache logs, custom PHP detection engine, threat_events tableسجلات Apache، ومحرك كشف PHP مخصص، وجدول threat_events
- Stream 2المسار 2
- Wazuh Windows agent, Ubuntu manager, webhook, threat_events tableعميل Wazuh على Windows، ومدير على Ubuntu، وWebhook، وجدول threat_events
- Enrichmentالإثراء
- AbuseIPDB reputation checkفحص سمعة AbuseIPDB
- Alertingالتنبيه
- Telegram bot, plus a weekly reportبوت Telegram، وتقرير أسبوعي
- Hostingالاستضافة
- cPanel, PHP + MySQLi, phpMyAdmin; Wazuh 4.14 on Ubuntu Server 24.04 LTS in EVE-NGcPanel وPHP مع MySQLi وphpMyAdmin؛ وWazuh 4.14 على Ubuntu Server 24.04 LTS في EVE-NG
How an alert travelsكيف يمر التنبيه
- Log ingestion: live Apache access logs are parsed.استقبال السجلات: تُحلَّل سجلات وصول Apache المباشرة.
- Rule-based detection: hits are tagged with a threat type and severity.الكشف بالقواعد: تُوسم الحالات المطابقة بنوع التهديد وخطورته.
- Endpoint visibility: Wazuh reports logon failures, account changes and file integrity events.رؤية الأجهزة: يبلّغ Wazuh عن فشل تسجيل الدخول وتغييرات الحسابات وأحداث سلامة الملفات.
- IP reputation: AbuseIPDB is checked before escalation.سمعة IP: يُفحص AbuseIPDB قبل التصعيد.
- Alerting: high-severity events go to Telegram, and a weekly report consolidates both sources.التنبيه: تذهب الأحداث العالية الخطورة إلى Telegram، ويجمع تقرير أسبوعي المصدرين.
Wazuh endpoint monitoringمراقبة الأجهزة بـ Wazuh
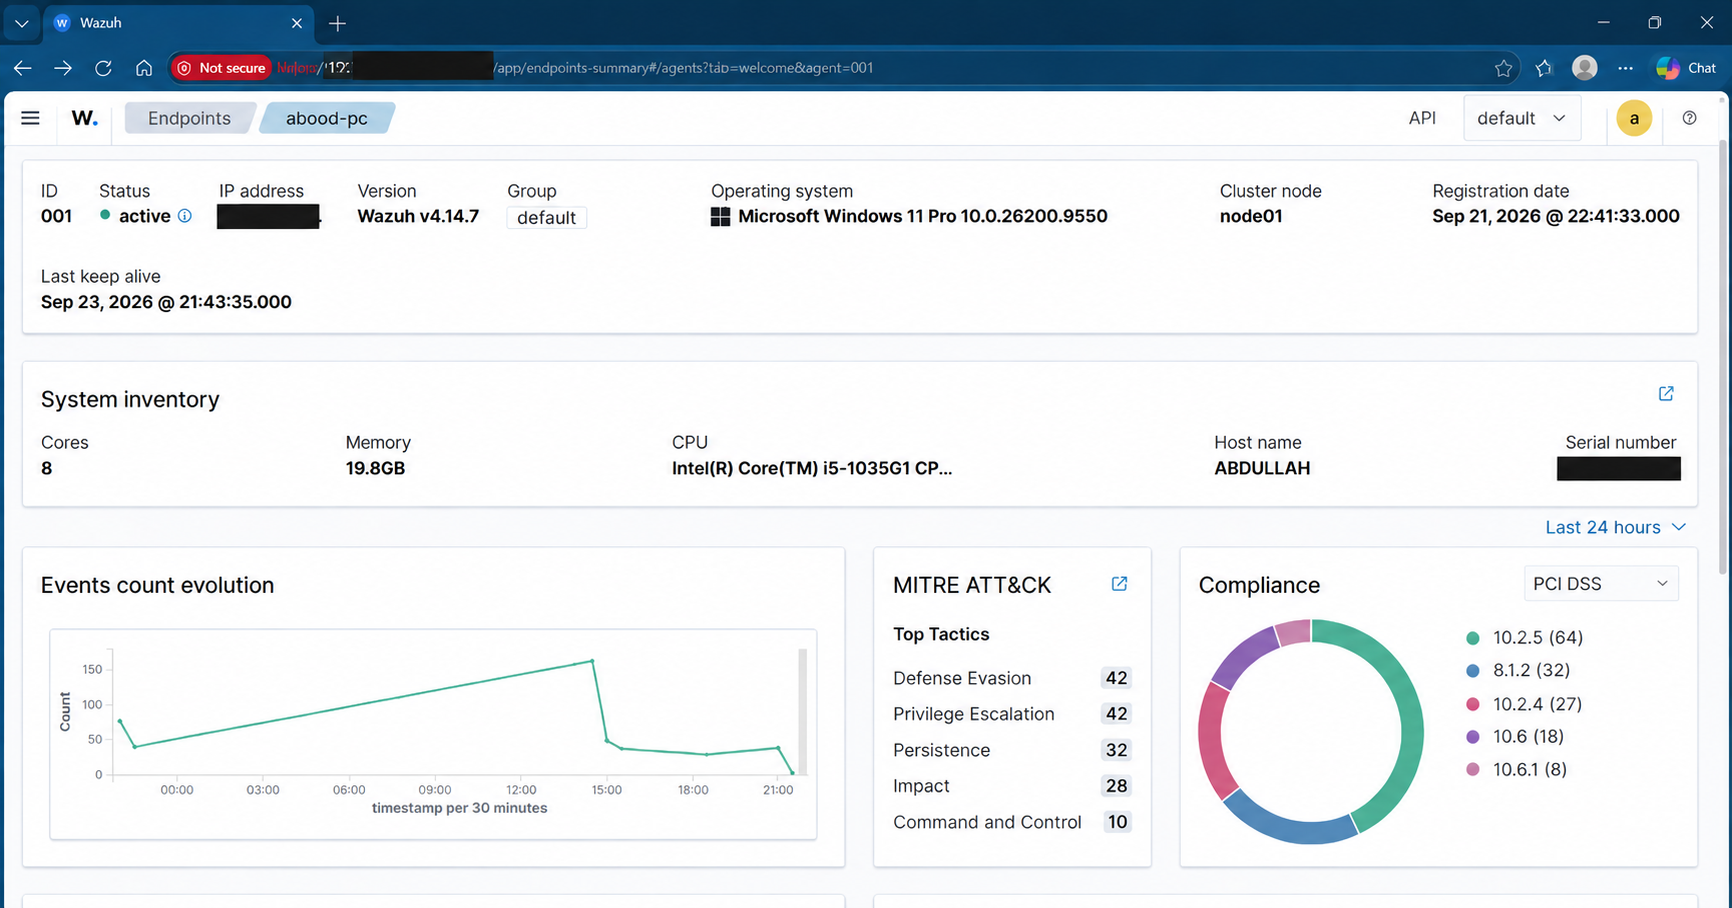
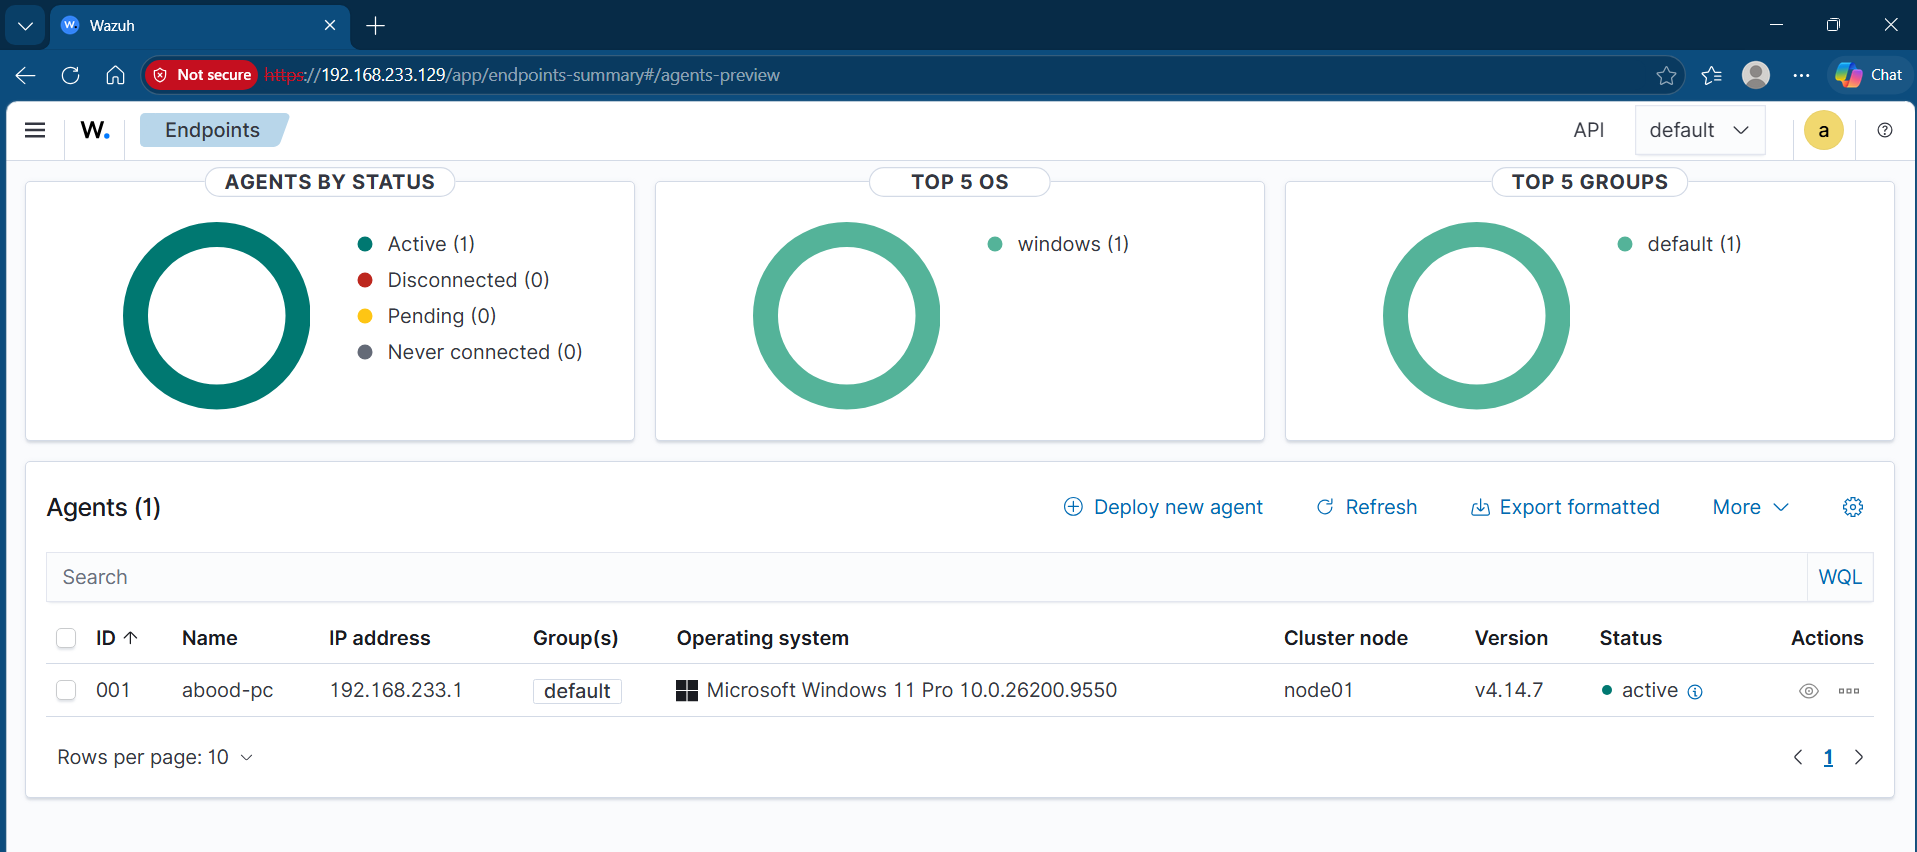
A Windows host reports to a Wazuh server running on Ubuntu in my EVE-NG lab. The dashboards show agent status, alert severity and MITRE ATT&CK tactics.جهاز Windows يبلّغ خادم Wazuh يعمل على Ubuntu في مختبر EVE-NG عندي. وتعرض اللوحات حالة العميل وخطورة التنبيهات وتكتيكات MITRE ATT&CK.
One shared timelineخط زمني مشترك
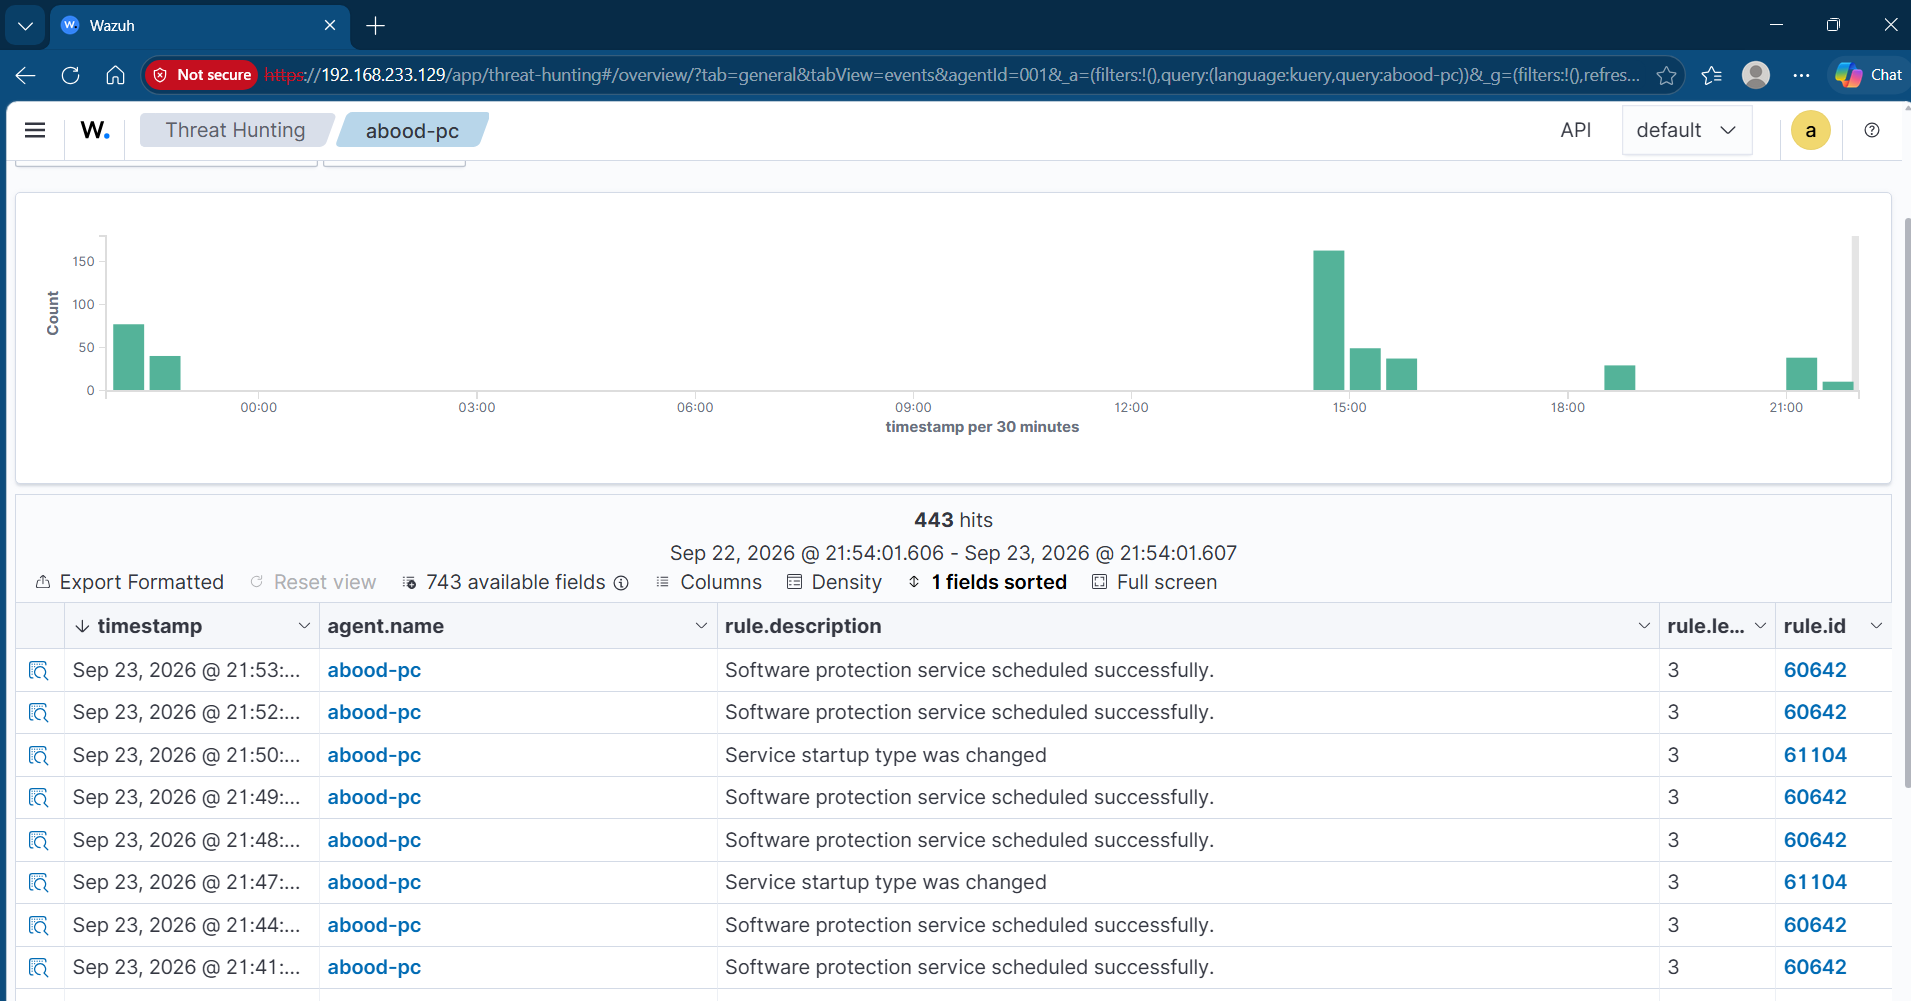
Wazuh alerts sit next to the platform’s own detections in the threat_events table. A forwarded Wazuh alert is stored with fields such as source, rule_id, rule_desc, level and agent_name.تجلس تنبيهات Wazuh بجانب كشوفات المنصة نفسها في جدول threat_events. ويُخزَّن تنبيه Wazuh المُمرَّر بحقول مثل source وrule_id وrule_desc وlevel وagent_name.
What went wrong, and the fixوش اللي تعطّل، وكيف انحلّ
- Webhook returned 401. The subdomain had cPanel directory password protection enabled at the Apache level, so every POST from Wazuh was rejected. I moved the ingest endpoint outside the protected path.الـ Webhook يرجّع 401. النطاق الفرعي كان عليه حماية كلمة مرور لمجلد في cPanel على مستوى Apache، فكل POST من Wazuh كان يُرفض. نقلت نقطة الاستقبال خارج المسار المحمي.
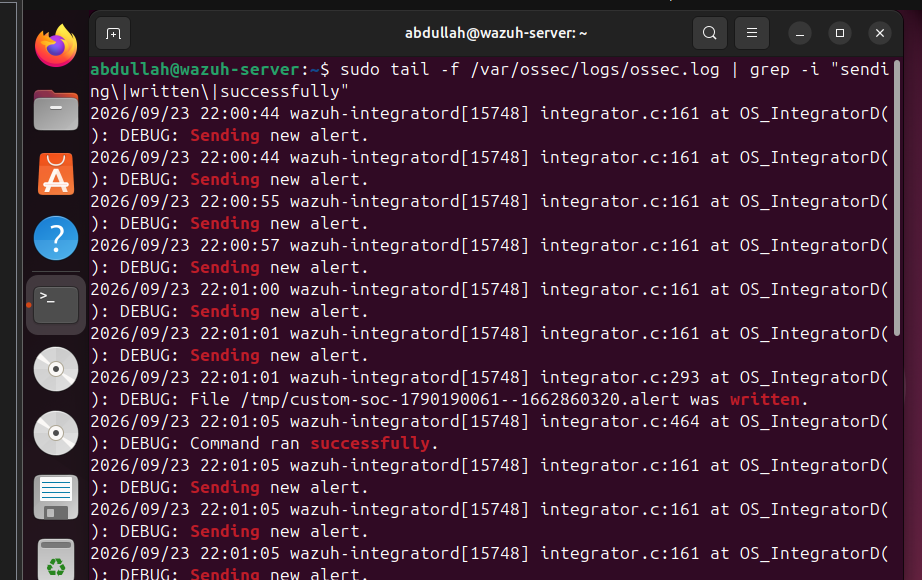
- The integration script looked dead. It only prints on error, so a clean run looked the same as a script that never ran. I enabled integrator.debug=2 and read the raw daemon logs to confirm it.سكربت التكامل كان يبان ميت. هو يطبع فقط عند الخطأ، فالتشغيل السليم يشبه سكربت ما اشتغل أصلاً. فعّلت integrator.debug=2 وقرأت سجلات الـ daemon الخام وتأكدت.
- Logon failures never arrived. Windows logon-failure events default to level 5, while brute-force correlation rules sit at 10 and above. I adjusted the threshold instead of re-checking the network.أحداث فشل الدخول ما كانت توصل. أحداث فشل الدخول في Windows افتراضياً عند المستوى 5، بينما قواعد ارتباط القوة الغاشمة عند 10 وأعلى. عدّلت العتبة بدل ما أعيد فحص الشبكة.
What this project showsما يُظهره هذا المشروع
- Building a detection pipeline from raw logs to alerts.بناء مسار كشف من السجلات الخام إلى التنبيهات.
- Integrating Wazuh with a custom webhook and database.ربط Wazuh بـ Webhook وقاعدة بيانات مخصصة.
- Enriching alerts with IP reputation and mapping to MITRE ATT&CK.إثراء التنبيهات بسمعة IP وربطها بـ MITRE ATT&CK.
- Debugging silent failures from daemon logs.تتبّع الأعطال الصامتة من سجلات الـ daemon.
Want the details behind this project?تريد تفاصيل أكثر عن هذا المشروع؟
I’m happy to walk through the design, the configs and what I would change in production.يسعدني شرح التصميم والإعدادات وما الذي سأغيّره في بيئة الإنتاج.